What’s new in Microsoft Security: September 2026
September 24, 2026 · Microsoft Security · Severity: LOW
AI agents are now running on employee devices, cloud platforms, and across developer workflows. Security teams need to see those agents, govern what they can reach, and contain them when something goes wrong. This month’s updates help you discover and control local AI agents, extend Zero Trust to agent traffic, and strengthen the security operations center (SOC) foundations that AI-era operations depend on. Here’s what’s new: Extend protection and support investigations with Microsoft Defender Bring more context into email investigation and hunting with Microsoft Security Copilot Available for.
AI agents are now running on employee devices, cloud platforms, and across developer workflows. Security teams need to see those agents, govern what they can reach, and contain them when something goes wrong. This month’s updates help you discover and control local AI agents, extend Zero Trust to agent traffic, and strengthen the security operations center (SOC) foundations that AI-era operations depend on.
Here’s what’s new:
Extend protection and support investigations with Microsoft Defender
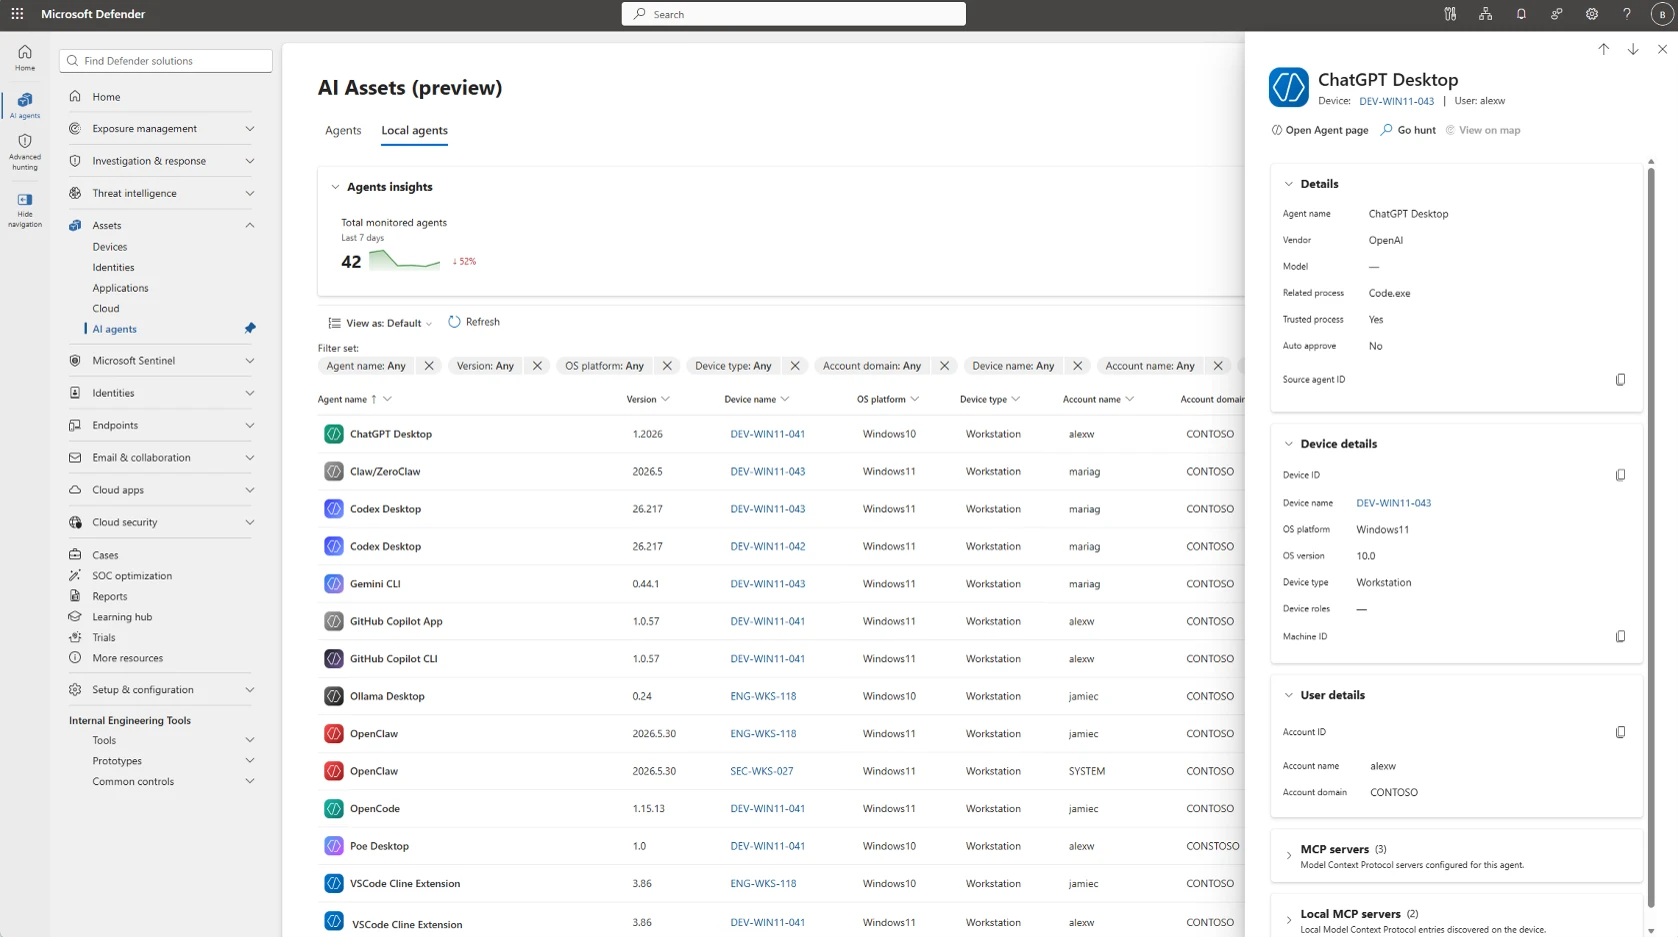
Bring more context into email investigation and hunting with Microsoft Security Copilot
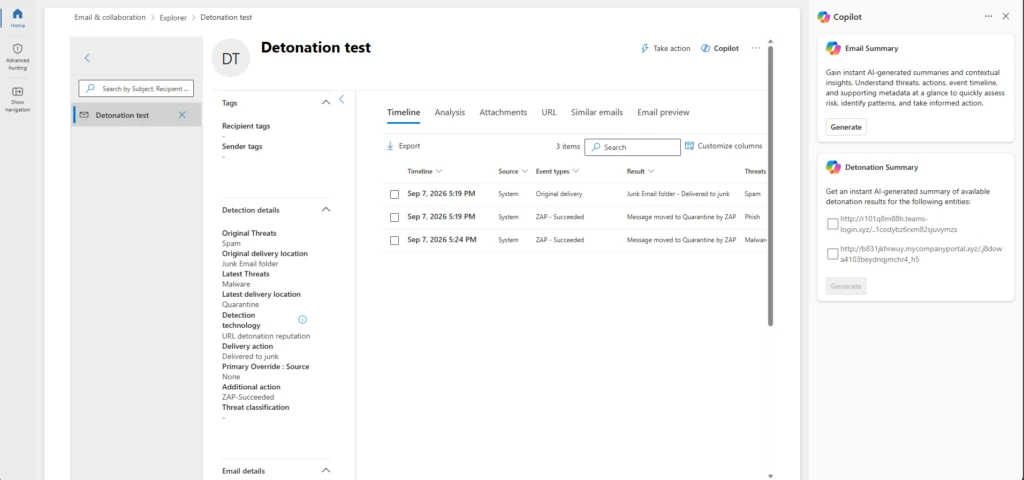
Available for organizations using both Microsoft Defender and Microsoft Security Copilot, a new email detonation summary delivers AI-generated explanations of URL and file sandboxing results, helping SOC teams investigate faster by reducing the manual effort required to correlate detonation evidence and contextual signals.
Protect sensitive data in motion with Microsoft Purview and Microsoft Entra
Stop sensitive data from reaching shadow AI over the network
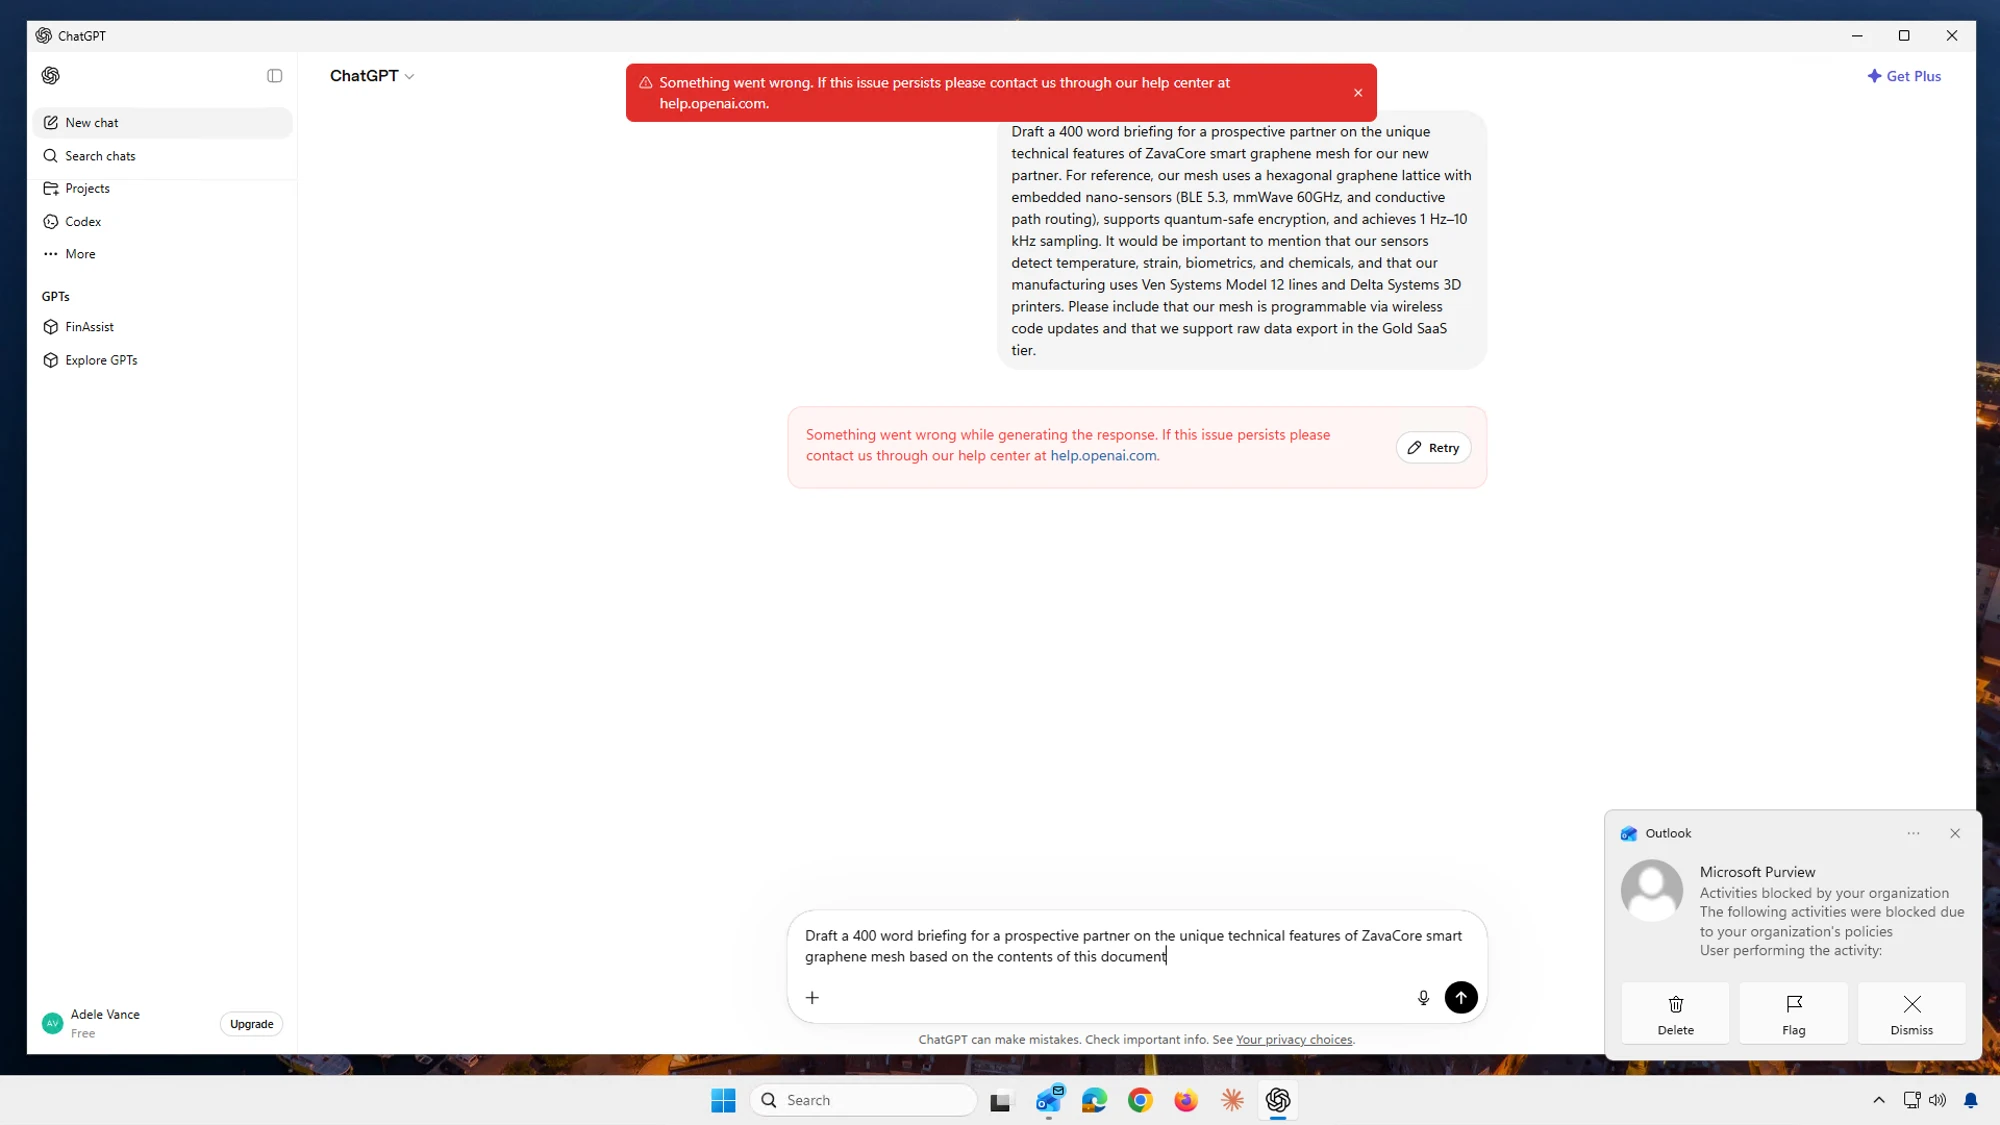
Now generally available, Microsoft Purview and Microsoft Entra Global Secure Access bring data security to the network across human actions and on-behalf-of (OBO) agentic traffic. Context-aware Microsoft Purview classification and policies are enforced by Entra at the network layer. Organizations can discover sensitive files and text in real time and block them from being shared to risky destinations. For example, if an employee or OBO agent tries to upload a sensitive document to an unsanctioned AI tool, the policy can stop the transfer before the data leaves.
Protect, investigate, and clean up enterprise data with Microsoft Purview
Manage labeling at enterprise scale with less administrative overhead
Microsoft Purview auto-labeling helps organizations automatically apply data security controls to sensitive content at enterprise scale. New auto-labeling enhancements improve policy scale, admin experience, and reporting. Policies now support simulations of up to 20 million items and up to 50,000 sites t
Key Takeaways
- Microsoft's September 2026 security roundup covers new products and features including enhanced threat detection capabilities and expanded platform integrations.
- Regular security update roundups help organizations stay informed about Microsoft's evolving security portfolio and relevant new capabilities.