The Good, the Bad and the Ugly in Cybersecurity – Week 35
August 28, 2026 · SentinelOne · Severity: MEDIUM
The Good | Authorities Launch New Operations Against Cybercrime Networks & Supply Chain Attackers Operation Jackal IV, coordinated by INTERPOL across 22 nations, has led to the arrest of 58 individuals and the identification of over 200 suspects linked to West African cybercrime networks . The joint action successfully dismantled elements of the Black Axe syndicate, which orchestrates global romance , investment, and business email compromise (BEC) scams.
The Good | Authorities Launch New Operations Against Cybercrime Networks & Supply Chain Attackers
Operation Jackal IV, coordinated by INTERPOL across 22 nations, has led to the arrest of 58 individuals and the identification of over 200 suspects linked to West African cybercrime networks. The joint action successfully dismantled elements of the Black Axe syndicate, which orchestrates global romance, investment, and business email compromise (BEC) scams. Law enforcement agencies across South Africa, Argentina, and Romania also disrupted major Crime-as-a-Service (CaaS) providers, freezing millions of dollars in illicit financial assets.
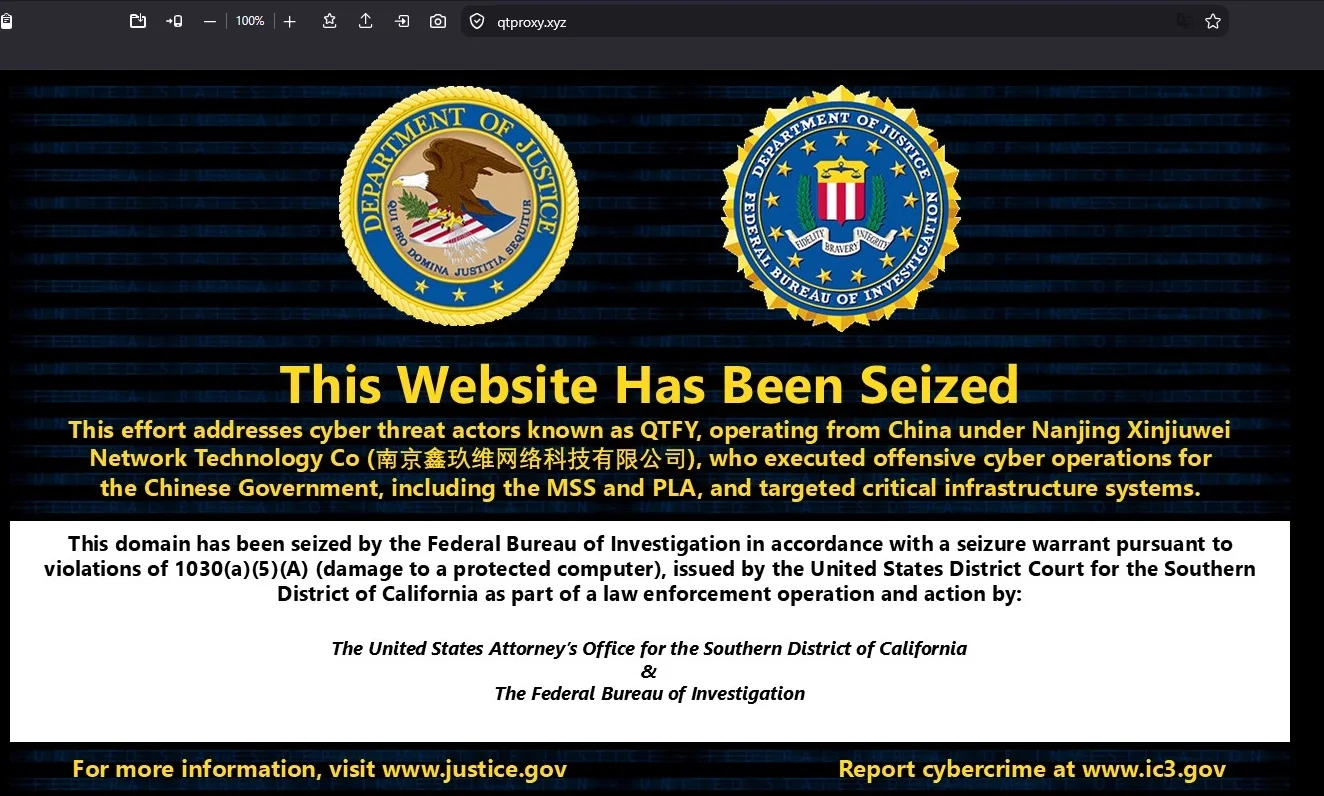
The FBI, collaborating with the DoJ, have disrupted the global QScan and QTRouter hacking platforms operated by Chinese state-sponsored threat actors. The group QTFY, which maintains direct ties to China’s military and intelligence services, used these compromised IoT botnets to mask cyber espionage traffic targeting critical U.S. networks, including the Federal Reserve and NASA. Law enforcement successfully seized the core command-and-control (C2) domains hardcoded within the malicious frameworks.
From the U.S. Treasury is a new operation dubbed Economic Outcast, imposing sweeping sanctions on five Mabna Institute members and nearly 60 Iran-linked entities. Under the direction of Iran’s Ministry of Intelligence and Security (MOIS), the attackers breached multiple American critical infrastructure organizations, state governments, and defense contractors. These state-sponsored actors then exfiltrated datasets, executed high-value cryptocurrency heists, and now face federal indictments alongside a $10 million dollar reward for information leading to their arrest.
The Australian Federal Police (AFP) have arrested and charged two individuals for principal roles in TeamPCP, a cybercrime syndicate. The group systematically compromised trusted open-source projects, including Trivy, Checkmarx KICS, and LiteLLM, by stealing developer credentials and distributing backdoored software updates across major ecosystem release channels. This massive software supply chain campaign potentially compromised organizations worldwide and facilitated the unauthorized theft of hundreds of thousands of credentials.
The Bad | ‘NovaCookies’ Phishing Toolkit Exploits DocuSign Services to Steal Session Tokens
Security researchers have disclosed details of NovaCookies, a subscription-based phishing platform that systematically targets corporate networks to steal authenticated Microsoft 365 sessions. Operating as an Adversary-in-the-Middle (AitM) proxy, this malicious toolkit is advertised on Telegram for $320 monthly. The campaigns actively compromise hundreds of organizations across several nations, including the U.S., the U.K., Germany, and the U.A.E.
To establish a foothold, attackers distribute counterfeit document-sharing lures within genuine DocuSign notifications. Styled as a share notice, the decoy claims an accounting department shared a remittance-advice PDF and invites the recipient to open it. Since these notifications originate from legitimate servers, they bypass standard sender-authentication checks and reputation filters. The malicious link is embedded inside the shared document, below the inspection layer of most security gateways. Once clicked, the attack uses an OAuth error-redirect technique to guide the browser through legitimate Microsoft or Google endpoints before routing traffic to the phishing infrastructure. This transition ensures every intermediate step appears trustworthy until the user reaches the proxy.
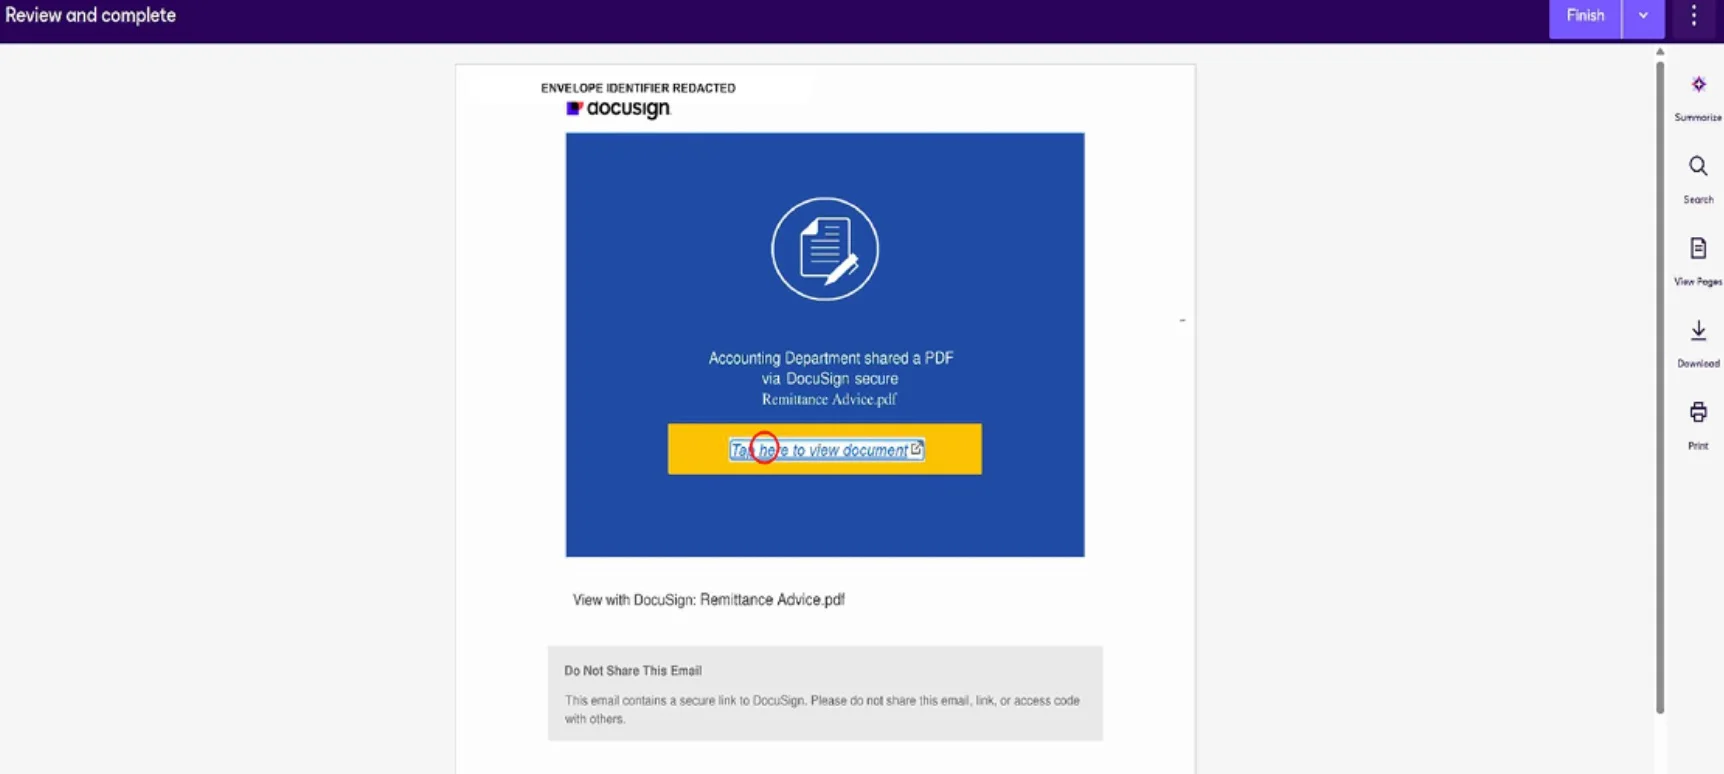
NovaCookies is a variant of the Sneaky2FA platform, which operates on a centrally managed model where the operator hosts the infrastructure rather than individual affiliates. The kit offers customized flows targeting common identity providers. Affiliates register landing pages on .vu domains, utilizing deceptive, alternating-case subdomains like PwPt-sHaRe to masquerade as legitimate Microsoft portals. While these checks obscure the landing pages, the proxy relays credentials and multi-factor authentication (MFA) codes in real time to Microsoft. Because each individual hop of the attack chain appears legitimate, security analysts emphasize that the browser remains the critical intersection where these events converge.
The Ugly | Threat Actors Deploy Spark RAT to Target Cambodian Organizations
A recently uncovered campaign is targeting both individuals and organizations in Cambodia with Spark RAT, which functions as a Go-based, open-source remote access trojan. Distributing compressed archives through targeted phishing emails, the threat actors deploy diverse lures, including Cambodian government notices, public health announcements, and dental records. The multi-stage attack sequence begins when a victim executes an Inno Setup installer, which initiates a dynamic link library side-loading chain using a signed Tencent application to deliver intermediate payloads.
To guarantee execution, the DLL loader performs timing-based anti-sandbox checks to det
Key Takeaways
- SentinelOne's weekly cybersecurity roundup covers notable threats, malware campaigns, and security industry developments from the past week.
- Key findings include new ransomware variants, vulnerability exploits, and emerging attack techniques observed in active campaigns.
- Organizations should review the full article for complete details and implement relevant security measures.