The Good, the Bad and the Ugly in Cybersecurity – Week 33
August 14, 2026 · SentinelOne · Severity: LOW
In a significant legal victory for cybersecurity, a UK court sentenced Justin Swaddle, a member of the decentralized cybercrime collective known as The Com, to two years in prison. Swaddle operated under the digital aliases Epstein, Rugen, and Moscow across platforms like Discord, Snapchat, and Telegram, and pleaded guilty to multiple charges of blackmail and child abuse. The National Crime Agency led the investigation that resulted in his conviction. Beyond the prison term, the court ordered Swaddle's placement on the National Sex Offenders Register, ensuring long-term monitoring of his activities. This case highlights ongoing efforts to dismantle online criminal networks that exploit vulnerable individuals through sextortion and blackmail schemes.
The Good | Courts Sentence “The Com” Online Syndicate Member for Blackmail & Sextortion
A court in the UK has sentenced a member of the decentralized online cybercrime collective known as “The Com” to two years in prison following an investigation by the National Crime Agency (NCA). Justin Swaddle, who operated under the digital aliases ‘Epstein’, ‘Rugen’, and ‘Moscow’ across Discord, Snapchat, and Telegram, pleaded guilty to multiple criminal charges of blackmail and child abuse. In addition to his sentence, the court ordered Swaddle’s placement on the National Sex Offenders Register and imposed a ten-year Sexual Harm Prevention Order.
Investigators revealed that Swaddle systematically targeted and groomed young, vulnerable victims globally, using popular chat platforms to exploit his targets. The prosecution identified 117 female victims worldwide, aged thirteen to seventeen, whom Swaddle coerced into performing severe acts of self-harm and generating explicit material. Rather than seeking financial gain, Swaddle was reportedly motivated by the online status and notoriety he obtained by sharing the media within exclusive subgroups. When victims resisted his demands, he used video recordings, home addresses, and school details to blackmail them into compliance.
The investigation, which the NCA initiated in January 2024 following Swaddle’s initial arrest by West Yorkshire Police, required extensive cross-border coordination. British officers collaborated closely with law enforcement agencies in the United States, Australia, Canada, Norway, and New Zealand to identify and safeguard affected children worldwide.
Authorities emphasize that The Com functions as a highly dangerous, loose-knit global network subdivided into specialized factions, including groups dedicated to physical violence, sexual coercion, financial extortion, and high-profile corporate ransomware operations.
The Bad | Agencies Warn of Expanding Gunra Ransomware Operations Targeting Critical Infrastructure
U.S., U.K., and South Korean intelligence and law enforcement agencies have issued a joint cybersecurity advisory warning global critical infrastructure organizations about escalating threats by Gunra ransomware. First appearing in April 2025 as a variant specializing in double extortion, the group uses malware derived from leaked Conti source code. Gunra targets public health, financial, and government sectors worldwide, with a heavy concentration of victims in Australia, East Asia, and Europe.
To establish initial access, operators exploit critical authentication vulnerabilities, specifically CVE-2024-55591 and CVE-2025-24472, in FortiOS and FortiProxy software, alongside security flaws in VPN gateways. While campaigns initially focused on Windows environments, the threat actors expanded to cross-platform operations by introducing a Linux variant. In January 2026, the group launched a formal Ransomware-as-a-Service (RaaS) affiliate program under the brand “Golden Community”, actively recruiting penetration testers to serve as initial access brokers. Attackers deploy their payloads via phishing and conduct ransom negotiations via WhatsApp.
Once inside a network, the actors utilize Impacket tools for credential dumping and lateral movement. They execute malicious tasks during nighttime hours, exfiltrating stolen documents to cloud services and deleting critical backup and archived data across primary and recovery centers. The malware leverages advanced ciphers like Salsa20 or ChaCha20 to encrypt terabytes of data in a limited timeframe.
Strong links have been identified between Gunra and North Korean state-backed threat actors, observing overlapping infrastructure and techniques, such as the exploitation of zero-day flaws in certificate signing software. Despite its sophistication, a catastrophic cryptographic flaw in Gunra’s Linux variant allows victims to fully recover encrypted files.
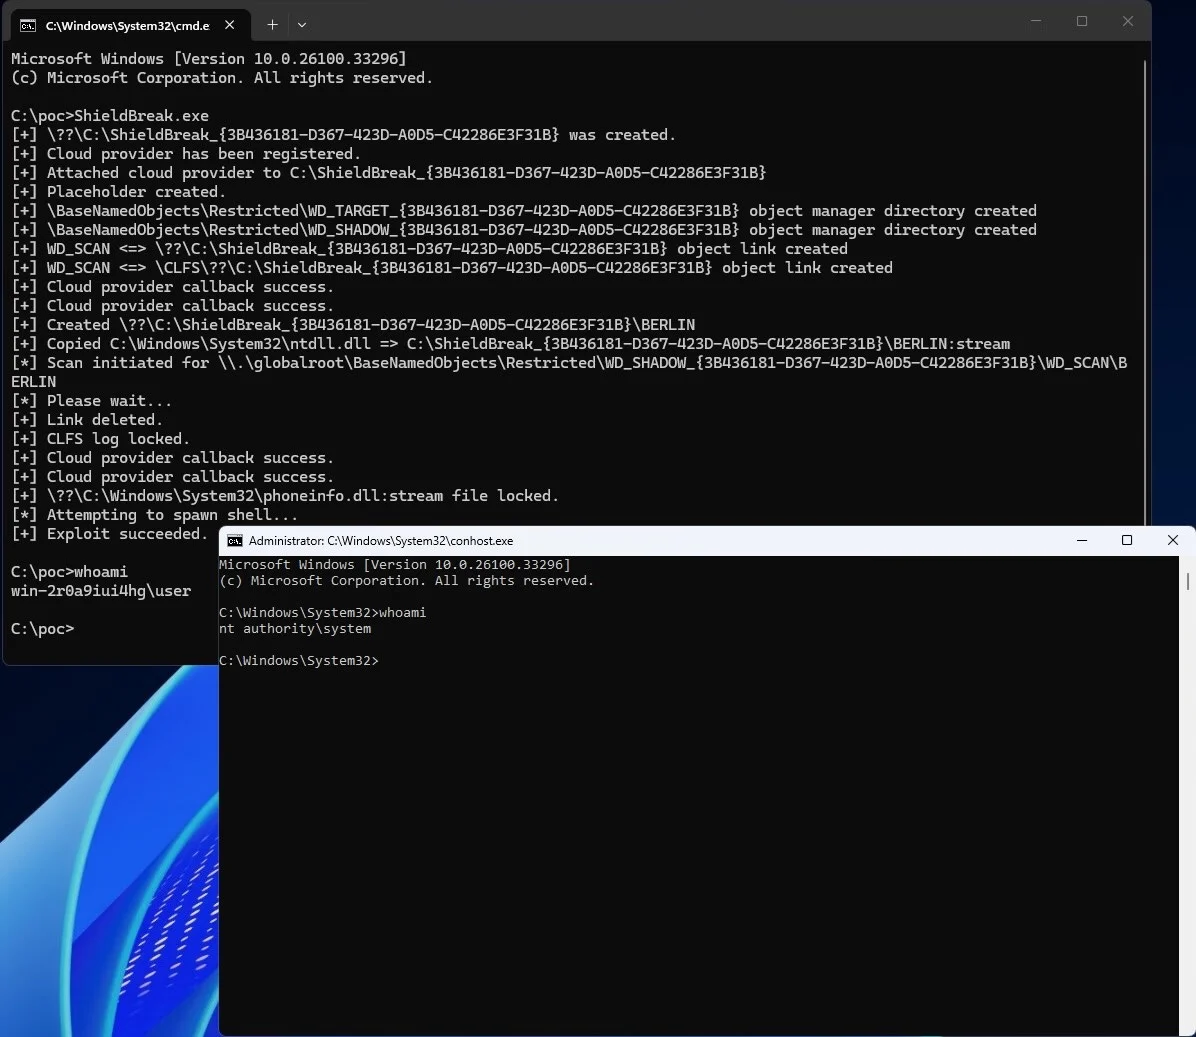
The Ugly | New ‘ShieldBreak’ Zero-Day Exploit Bypasses Microsoft Defender Protections
A security researcher known as ‘Nightmare Eclipse’ has released a novel Microsoft Defender zero-day exploit dubbed ‘ShieldBreak’ shortly after this month’s Patch Tuesday update. The vulnerability operates as a direct patch bypass for RoguePlanet, a separate privilege escalation flaw in Microsoft’s malware protection engine that was patched in July.
Key Takeaways
- A UK court sentenced Justin Swaddle of The Com syndicate to two years for blackmail and sextortion.
- Swaddle used aliases across Discord, Snapchat, and Telegram to commit crimes against minors.
- The court placed Swaddle on the National Sex Offenders Register following his guilty plea.