Least privilege for AI agents: Identity, access, and tool binding
July 16, 2026 · Microsoft Security · Severity: CRITICAL
Microsoft highlights the growing risks of AI agents operating without proper identity and access controls, emphasizing the need for least-privilege principles. AI agents, which autonomously chain actions across systems, can inadvertently access or modify sensitive data if assigned overly broad permissions. Common missteps include provisioning agents with excessive "Reader" roles that later expand to write access, or granting cross-tool access that enables unintended data correlation. These gaps can lead to unauthorized actions, privilege escalation, and auditability challenges, complicating incident response and regulatory compliance. To mitigate risks, Microsoft recommends treating AI agents as first-class security principals with managed identities, least-privilege RBAC, and tightly scoped tool access. Best practices include assigning unique agent identities with clear ownership, task-based roles, and controlled tool manifests. Time-limited entitlements (e.g., JIT elevation) should restrict permissions to specific workflows, while maintaining stable identities for lifecycle management. Without these controls, organizations risk incidents where accountability is unclear, leaving leadership unable to explain actions to customers or auditors.
AI agents aren’t only smarter API callers. They plan, chain actions across systems, and invoke tools in sequences while no single human explicitly approves each step. The architectural reality may introduce identity and authorization challenges that organizations are still evolving to address.
When an agent operates without a managed identity and least-privilege role-based access controls (RBAC), it can access or modify sensitive data beyond intended permissions if controls are not properly configured. Since agents can operate across multiple systems within a single workflow, a misconfigured permission may increase the potential impact compared to traditional service account scenarios, depending on how the system is configured and scoped. Organizations are deploying agentic capabilities (multi-step automation, delegated actions, tool use) faster than their identity and authorization models are evolving to safely constrain them.
The resulting exposure can be significant and may include risks such as unauthorized data access, unintended writes or deletions, and potential privilege escalation arising from overly broad role assignments. In some cases, these conditions can also contribute to gaps in auditability, which may make cyberattack detection, incident response, and regulatory inquiries more complex than necessary.
The right mental model is to treat every agent as a first-class principal: give it a lifecycle-managed identity, assign explicit roles, scope its permissions tightly, and scope tool usage to a preconfigured tools manifest or configuration.
Real-world scenarios
The risk can occur in real-world implementations. Consider a common pattern: a team provisions an agent with a broad “Reader” role because it’s quick and the initial use case seems read-only. Then the workflow expands to include fixing issues it finds, and suddenly the agent needs write access too. Rather than rethinking the role design, teams grant something broader than intended and move on.
The scope creep is quiet, incremental, and rarely revisited. A related problem emerges when agents work across multiple tools. An agent with access to email, files, a ticketing system, and a code repository may look low-risk at each individual integration, but the combination lets it correlate data across systems and take actions no one explicitly authorized as a whole. Combined access across systems may result in broader effective permissions than evaluated individually.
Underneath both scenarios is a question that teams consistently fail to answer cleanly: is the agent acting under its own identity, a delegated user scope, or some mix of both? That ambiguity matters because it determines who’s accountable when something goes wrong, and what approvals were actually required.
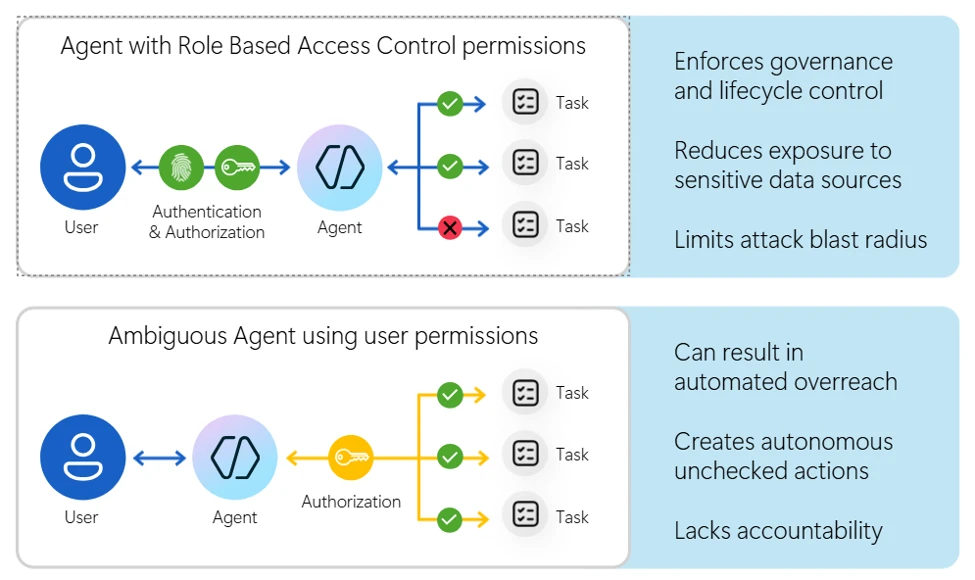
When the answer isn’t documented and enforced upfront, it shows up later in the worst possible context: an incident where logs might capture what tool was called but can’t answer key questions such as: who authorized the action, under what role, or whether it was within intended scope. Sensitive data may be retrieved or summarized beyond its intended audiences if controls are not properly scoped.
An agent helpfully automates a remediation step and modifies or deletes something it shouldn’t have. Then the investigation stalls not because logs are missing, but because the identity model was never coherent enough to make them meaningful. This leaves organizations in the firefighting mood to resolve and solve questions their leadership cannot fully answer to customers, press, or auditors.
Best Practices: Identity + RBAC + Scope + Safe Tool Binding
For best practices in designing agentic identity and authorization, implementing multiple controls is intended to help reduce the potential impact of agent actions when configured and applied appropriately, while helping make privilege decisions explicit and supporting accountability in the event of unexpected or unintended outcomes.
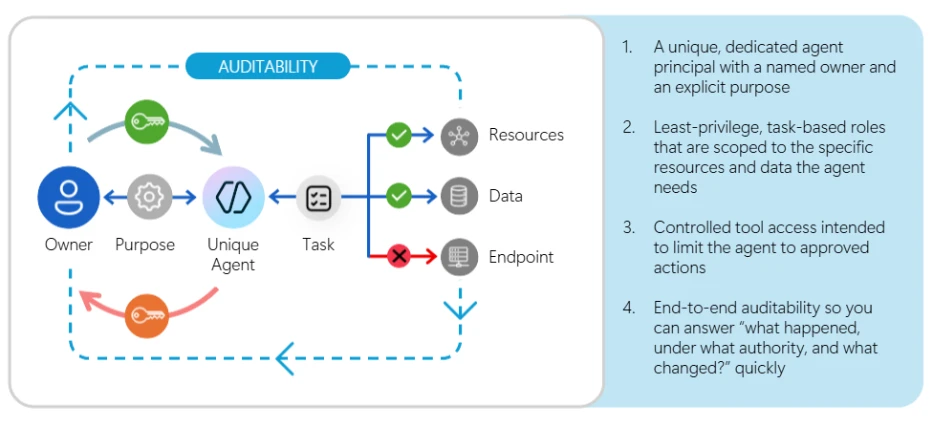
Recommended practices for teams are generally to establish and document:
(1) a unique, dedicated agent principal with a named owner and an explicit purpose
(2) least-privilege, task-based roles that are scoped to the specific resources and data the agent needs
(3) Controlled tool access intended to limit the agent to approved actions
(4) end-to-end auditability so you can answer “what happened, under what authority, and what changed?” quickly.
In practice, the time-limited aspect should typically apply to entitlements (role activation, tokens, or approvals) rather than trying to create a new identity for every task. Most real-world deployments keep the agent identity stable for lifecycle management, while using just-in-time (JIT) elevation to grant narrowly scoped privileges only for the duration of a specific workflow.
Start by making the agent afirst-class principal. Create a dedicated agent identity (not a shared secret or reused service account), document its purpose statement (“what it is allowed to do and why”), and assign clear human ownership for approvals and incident response.
Build in lifecycle management from day one: onboarding checks, credential rotation, suspension/decommissioning procedures, and a fast shutdown mechanism that actually invalidates credentials and tokens. Then design role-based access controls (RBAC) around discrete tasks, not teams or org charts.
Model roles that match the smallest meaningful units of work, such as “Read-only knowledge retrieval,” “Summarize labeled documents,” “Create a draft ticket.” Avoid bundling unrelated permissions to reduce operational friction. When the workflow includes both evidence gathering and remediation, separate duties: use different roles (or different tools) for read versus write, and gate high-impact actions like delete, export, or privilege changes behind step-up approvals.
Scope everything and do it multiple times. Constrain permissions by resource boundary (tenant/subscription/workspace/site), by data boundary (collection, label, sensitivity), and by operation boundary (read/write/export/admin).
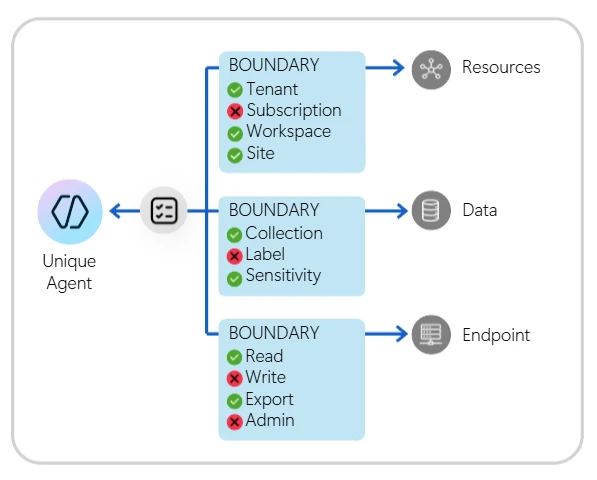
The goal is to help make the where and what of access as explicit as the who. Pair this with safe tool binding by exposing a curated and approved set of tools/actions to the agent, and require explicit allowlists for high-impact operations.
Key Takeaways
- Apply least privilege to AI agents to limit potential damage.
- Use identity and RBAC to control agent permissions.
- Implement safe tool binding to prevent misuse.