From Raw Threat Reports to Actionable Defense: AI-Powered Deep Threat Research
September 7, 2026 · SOCPrime · Severity: MEDIUM
Security teams are drowning in threat reports. Every week brings a new advisory, a new vendor write-up, a new blog post describing the latest campaign — and every one of them demands hours of manual reading, cross-referencing, and translation into something your SOC can actually act on.
Security teams are drowning in threat reports. Every week brings a new advisory, a new vendor write-up, a new blog post describing the latest campaign — and every one of them demands hours of manual reading, cross-referencing, and translation into something your SOC can actually act on. Deep Threat Research changes that equation entirely.
Deep Threat Research is an agentic AI tool available within Agentic Threat Research mode in Prime Architect. It takes any threat report and instantly transforms it into structured, decision-ready threat intelligence — complete with a clear threat summary, precise MITRE ATT&CK mappings, and a full set of interactive visualizations that show exactly how an adversary operates. What used to take an analyst hours of manual triage now happens in minutes, freeing your team to focus on what matters most: threat detection and threat mitigation.
What Deep Threat Research Solves
Every threat report contains value, but that value is locked inside dense paragraphs of prose. Deep Threat Research unlocks it automatically. It reads the report the way your most experienced analyst would — extracting the adversary’s tactics, techniques, and procedures, identifying relevant indicators, and mapping everything against the MITRE ATT&CK framework — then hands you a complete intelligence package: investigation guidance, mitigation recommendations, response actions, associated threat actors, and even AI-generated detection rules ready for deployment.
Instead of starting from a blank page, your team starts from a fully-formed picture of the threat: who’s behind it, how it moves, what it touches, and how to stop it.
What You Get
Once an analysis completes, results are generated and appear one after another. Some sections are ready to read right away, while others display as tiles you simply click to open and explore in more detail — just scroll down to move through the full analysis. Overall, Deep Threat Research organizes its findings into clear, digestible sections:
- Summary – the essential facts of the threat, distilled from the report
- Investigation – guided next steps for analysts
- Mitigation – best-practice actions to reduce impact
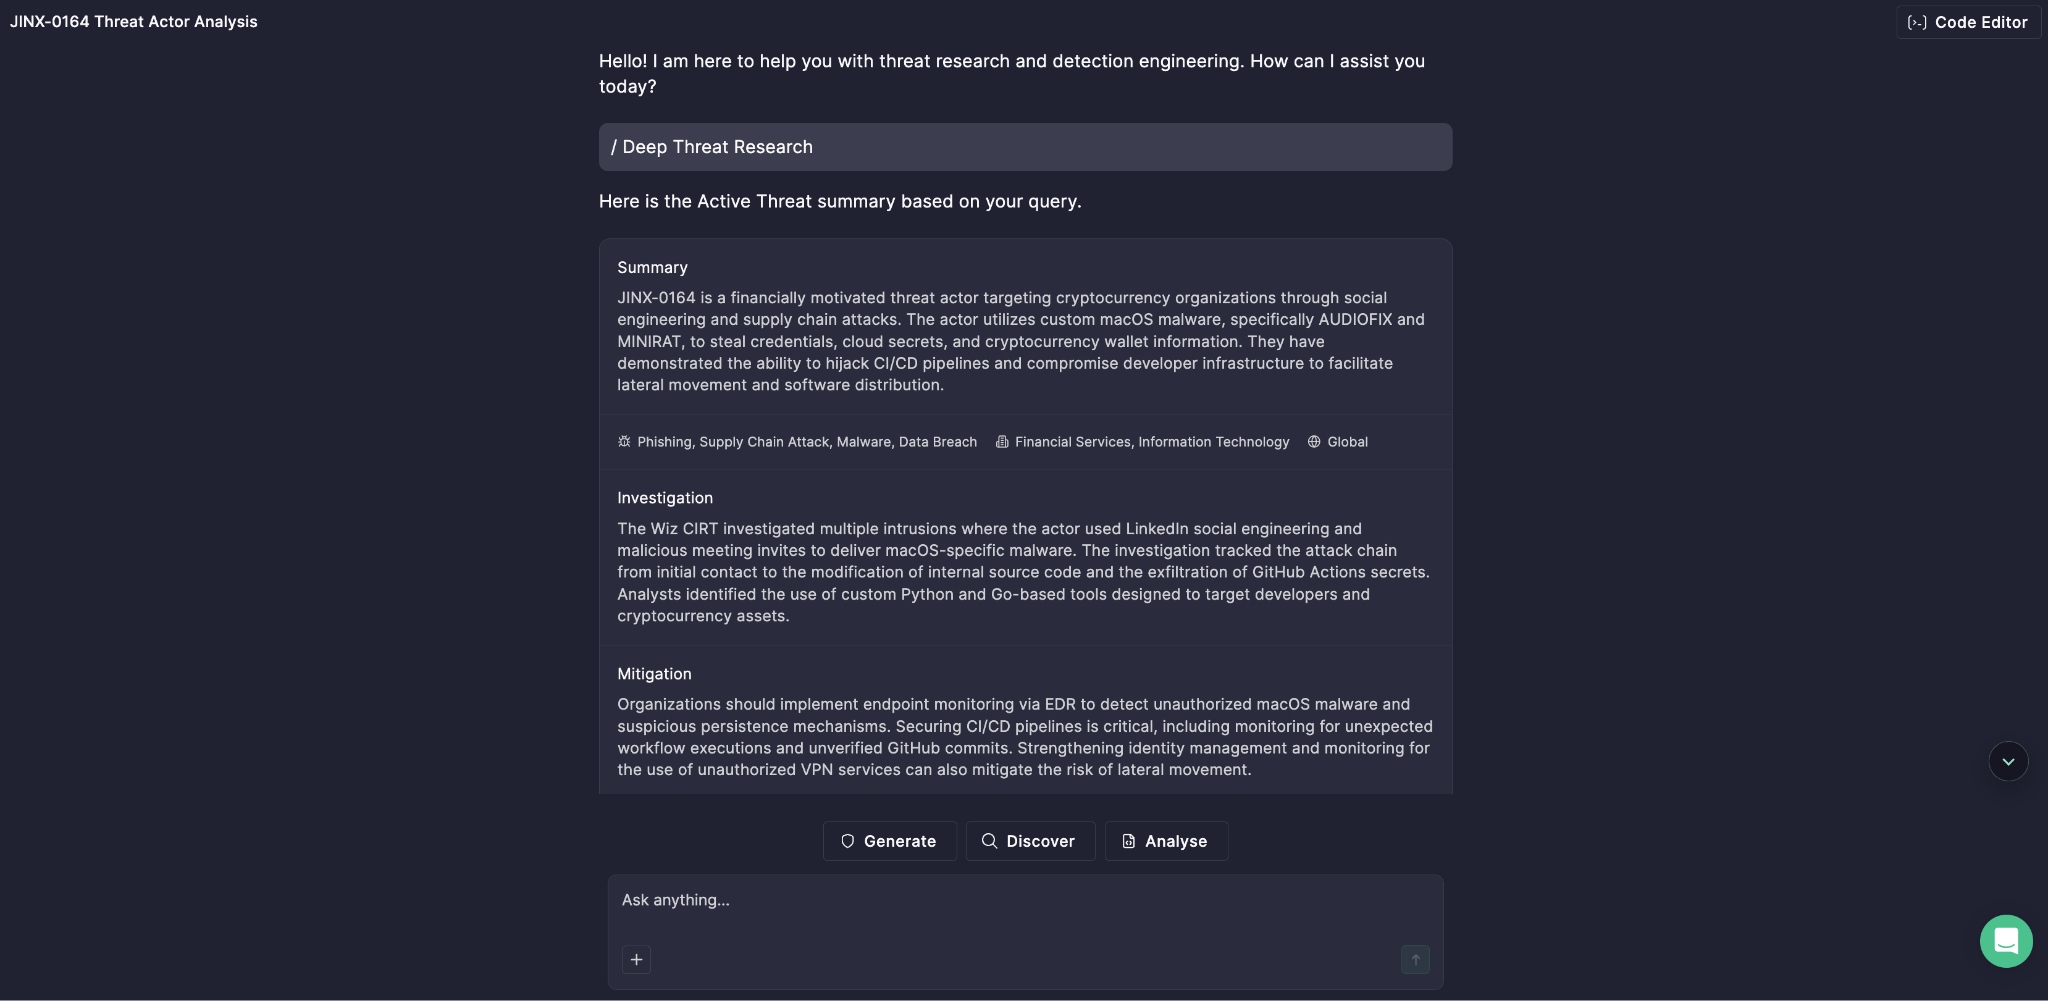
- Response – recommended steps once malicious activity is confirmed
- Actors – the threat actors tied to the activity
- MITRE ATT&CK Techniques – the specific behaviors and techniques adversaries used, mapped directly to the framework
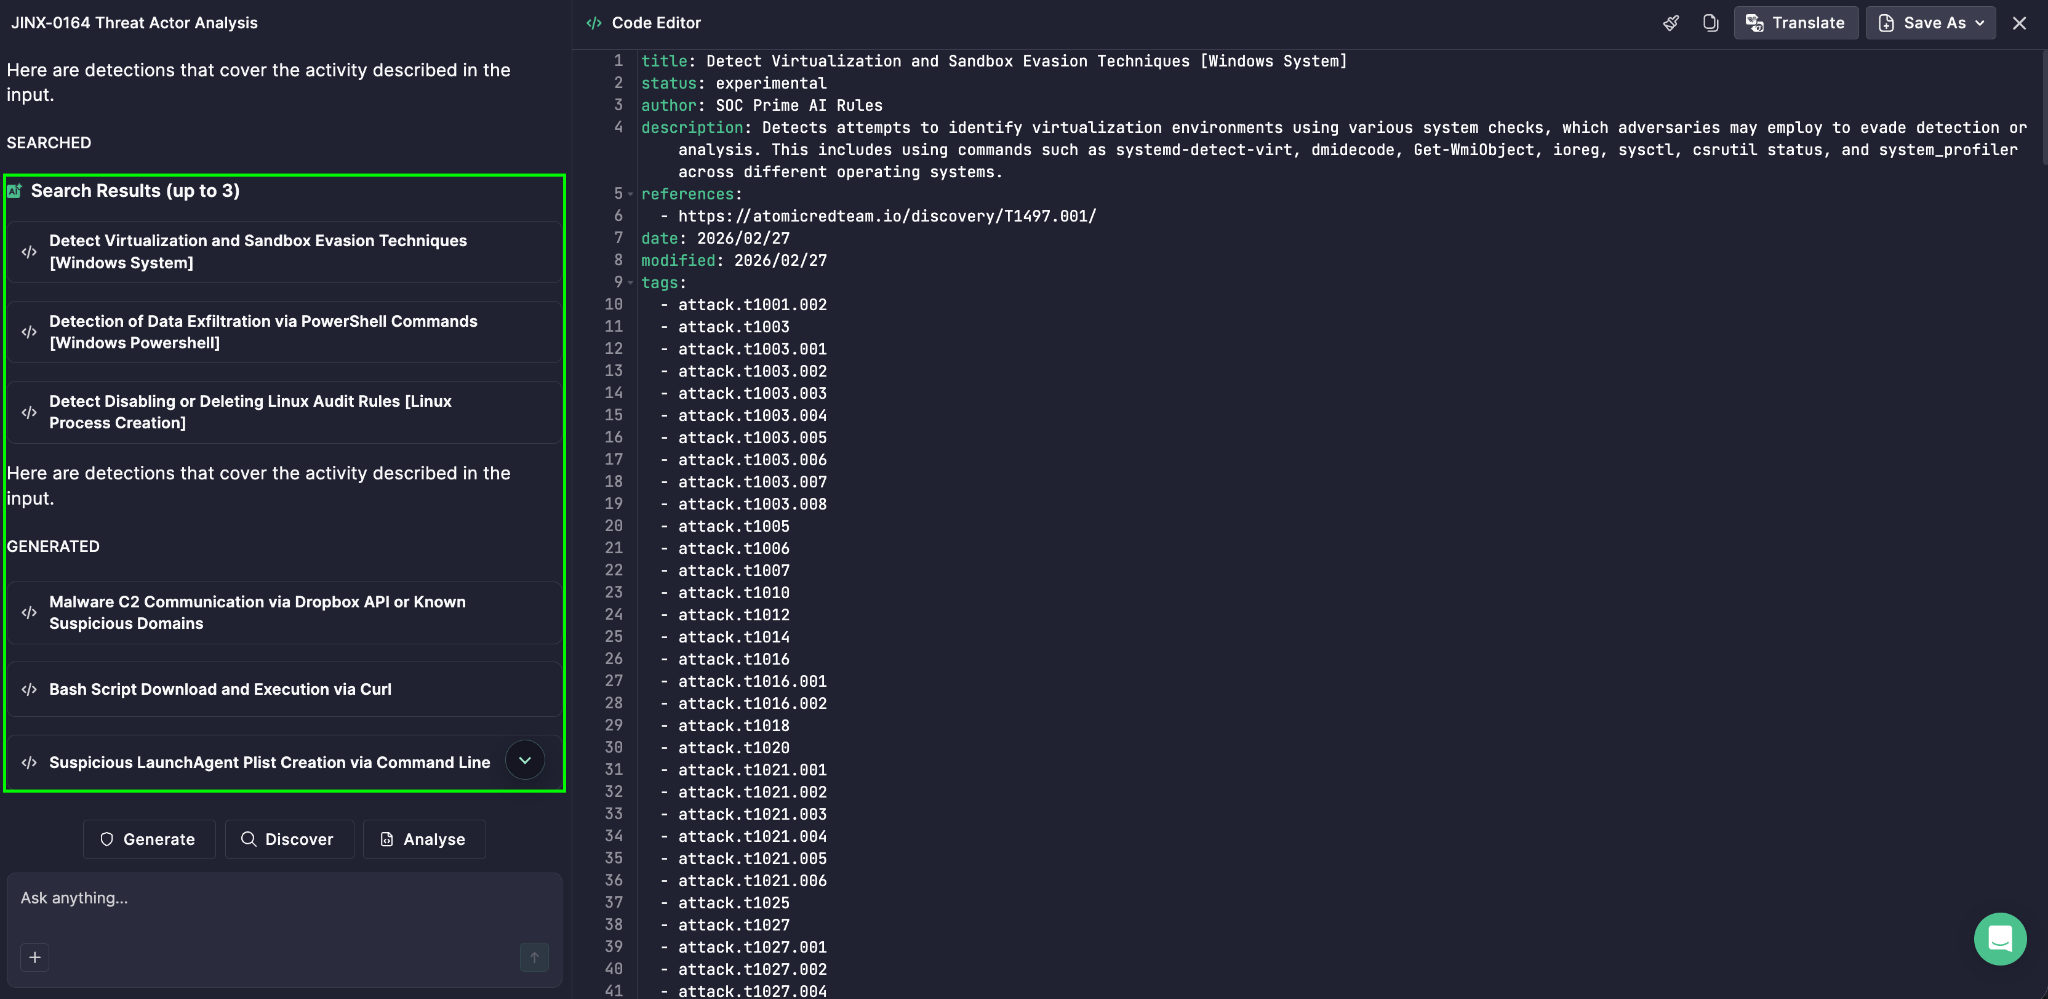
- Detections – existing SOC Prime Platform detections plus new AI-generated rules, ready to copy, translate into your SIEM’s language, validate, or save straight to your repository
- Simulation – ready-made simulations of the malicious activity for testing your defenses
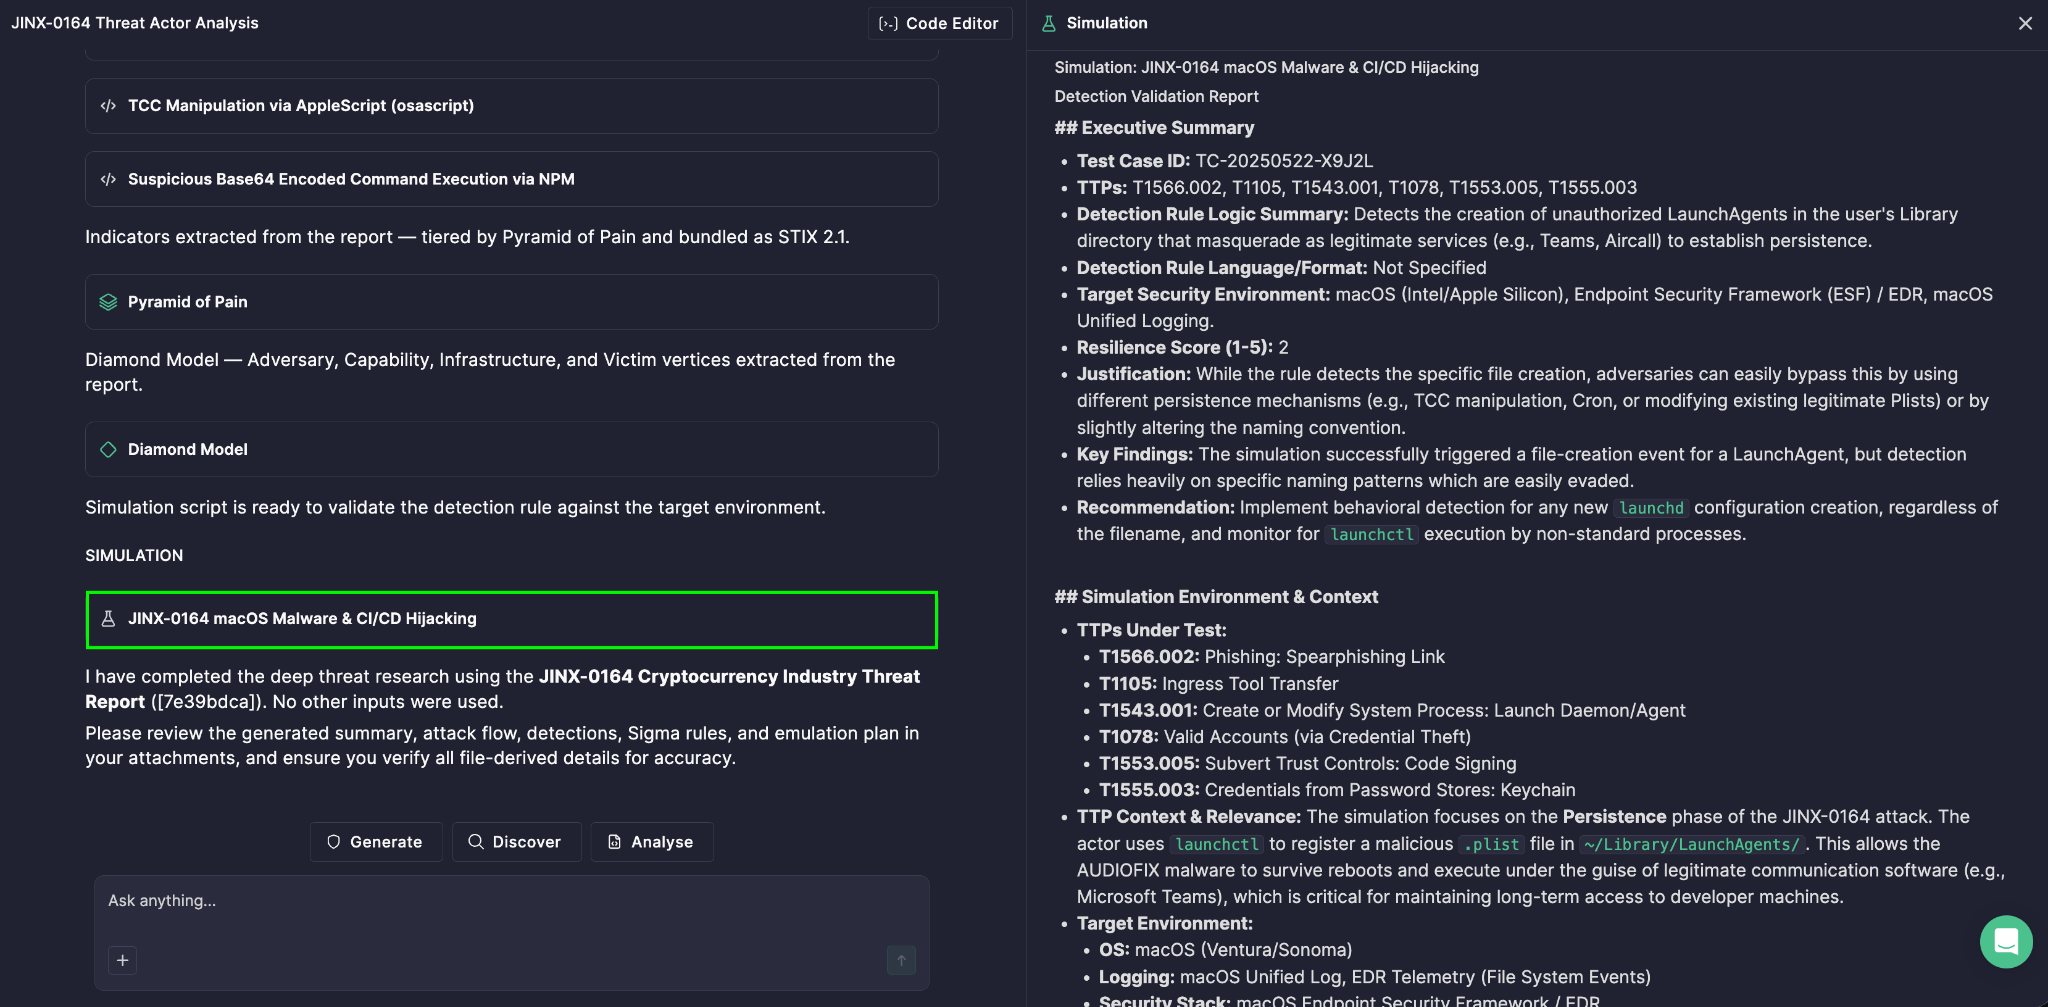
On top of that, four interactive visualizations bring the intelligence to life:
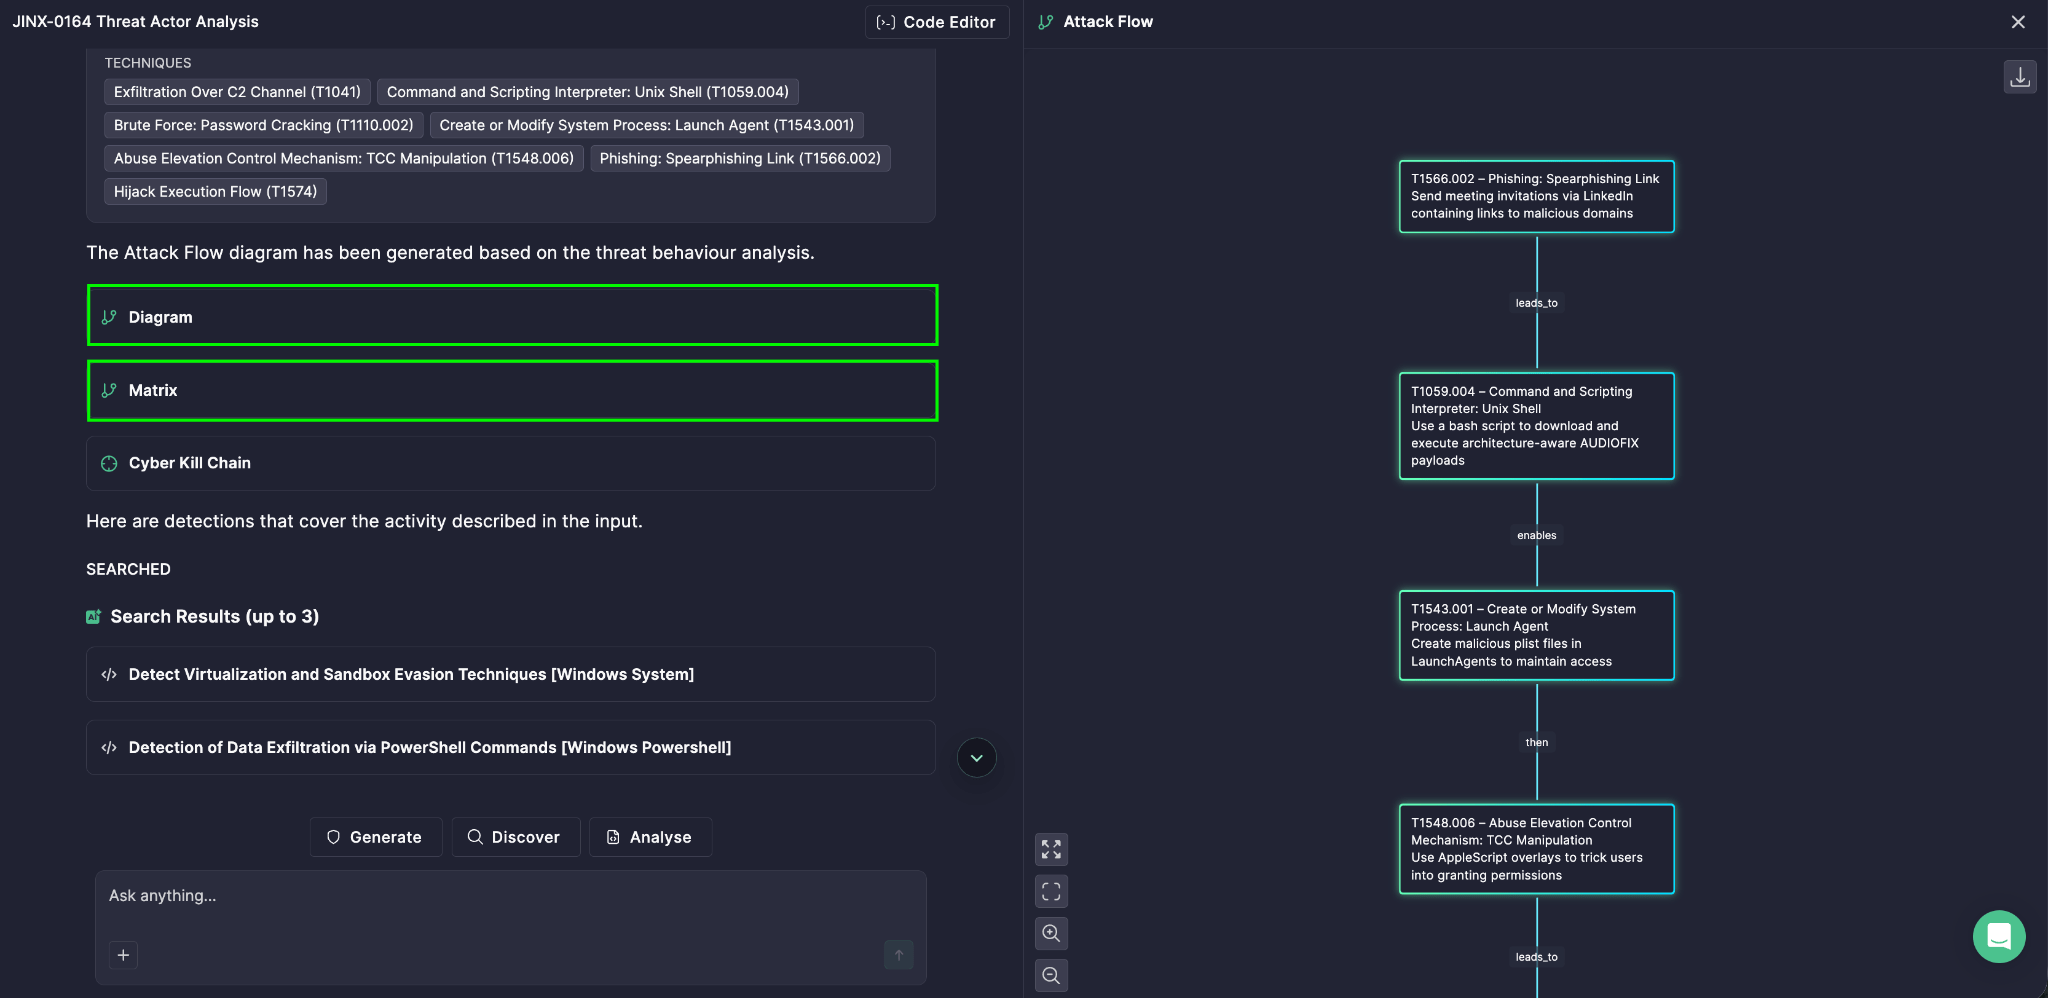
- Attack Flow – the adversary’s full attack sequence based on MITRE ATT&CK, viewable as a diagram or matrix and exportable as MMD
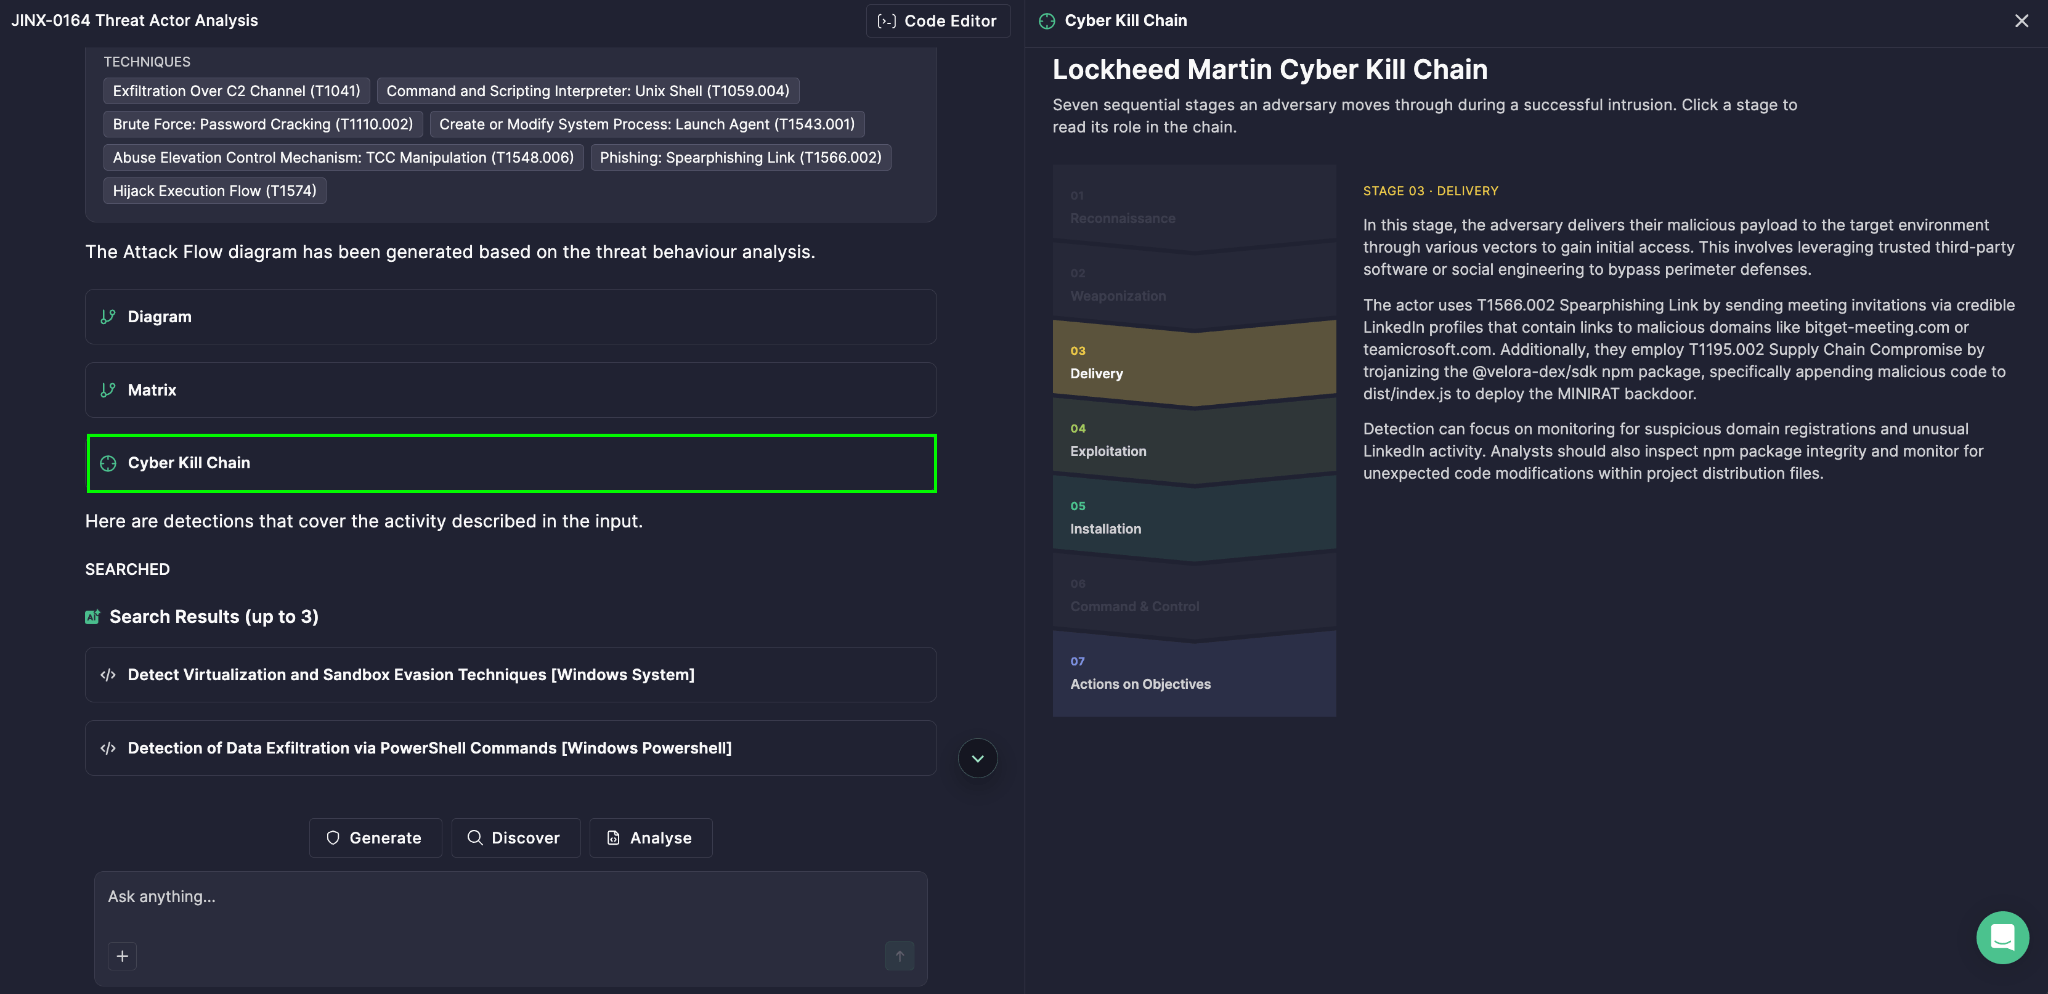
- Cyber Kill Chain – maps the threat across all seven Lockheed Martin stages, from Reconnaissance to Actions on Objectives, so you can spot detection opportunities at every phase
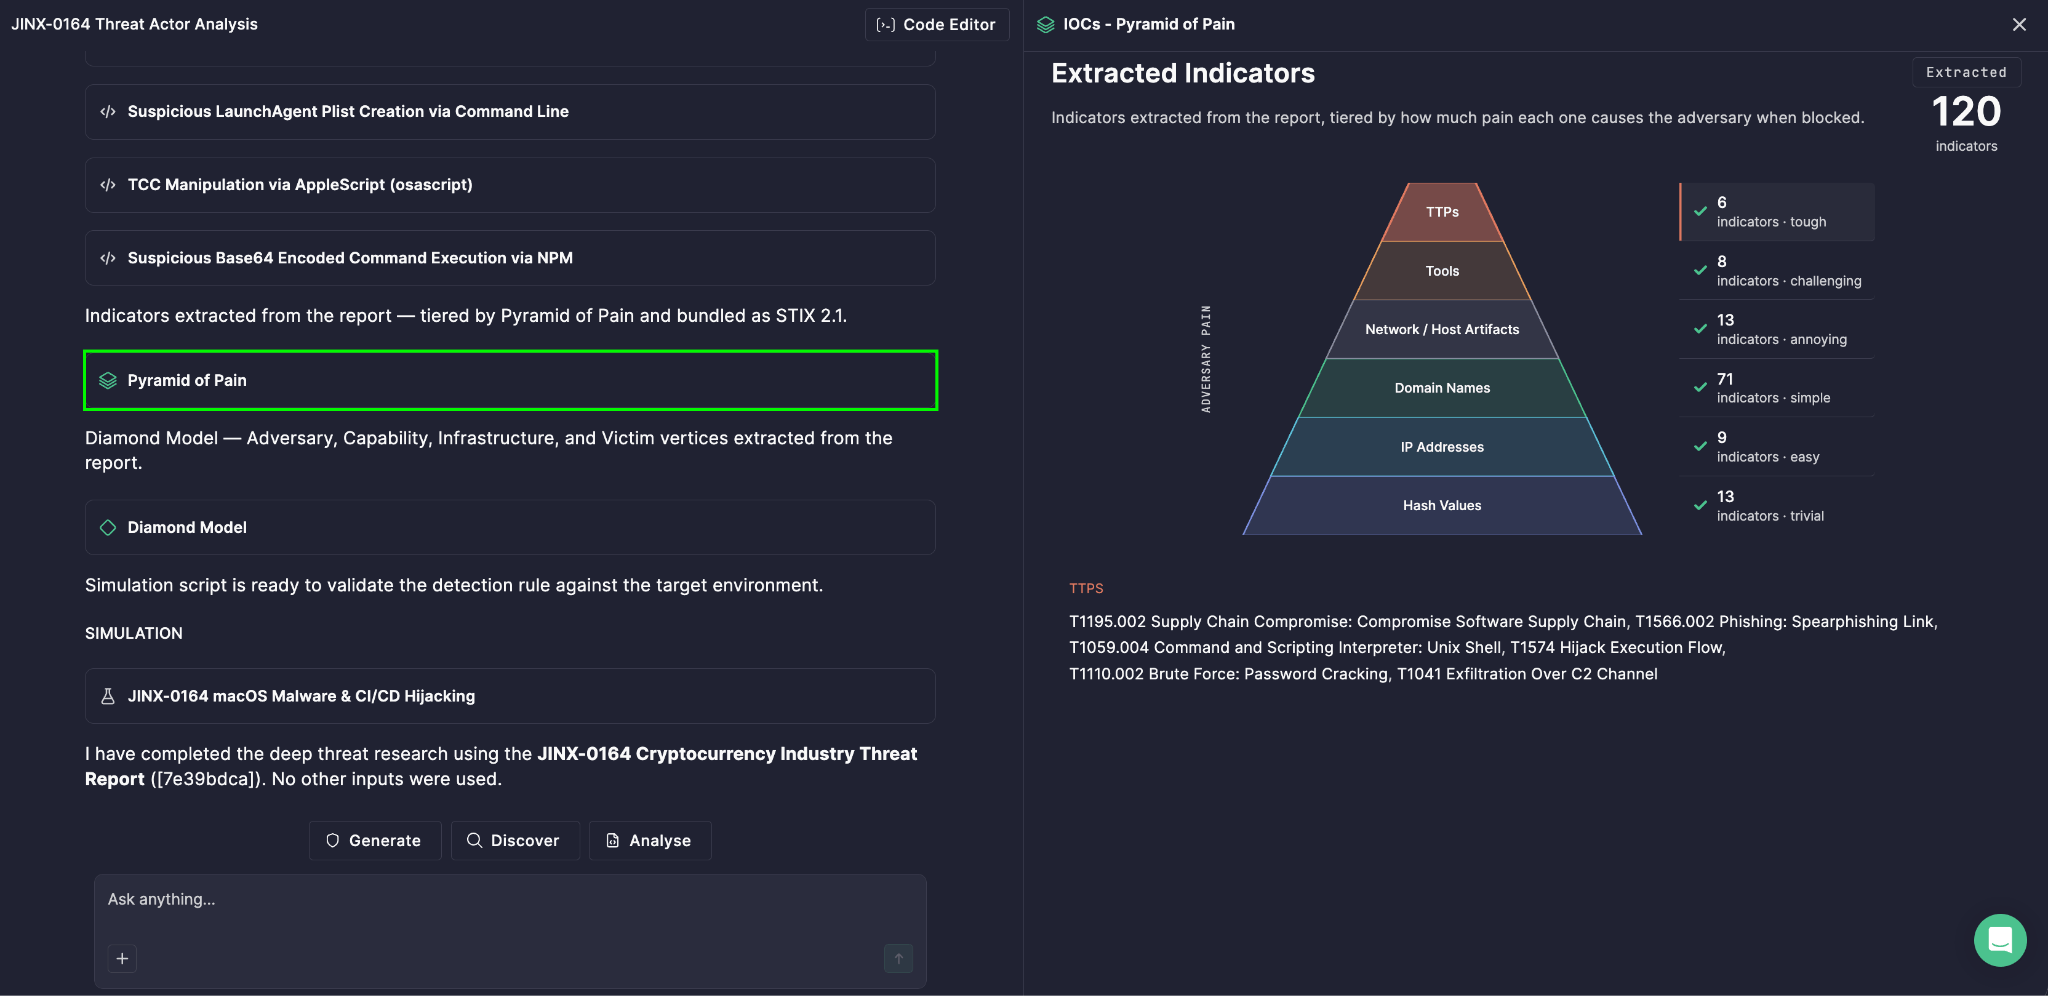
- Pyramid of Pain – breaks down every extracted indicator into six tiers, from Hash Values and IP Addresses up through Domain Names, Network/Host Artifacts, Tools, and TTPs, so you can see at a glance how resilient your detection coverage really is
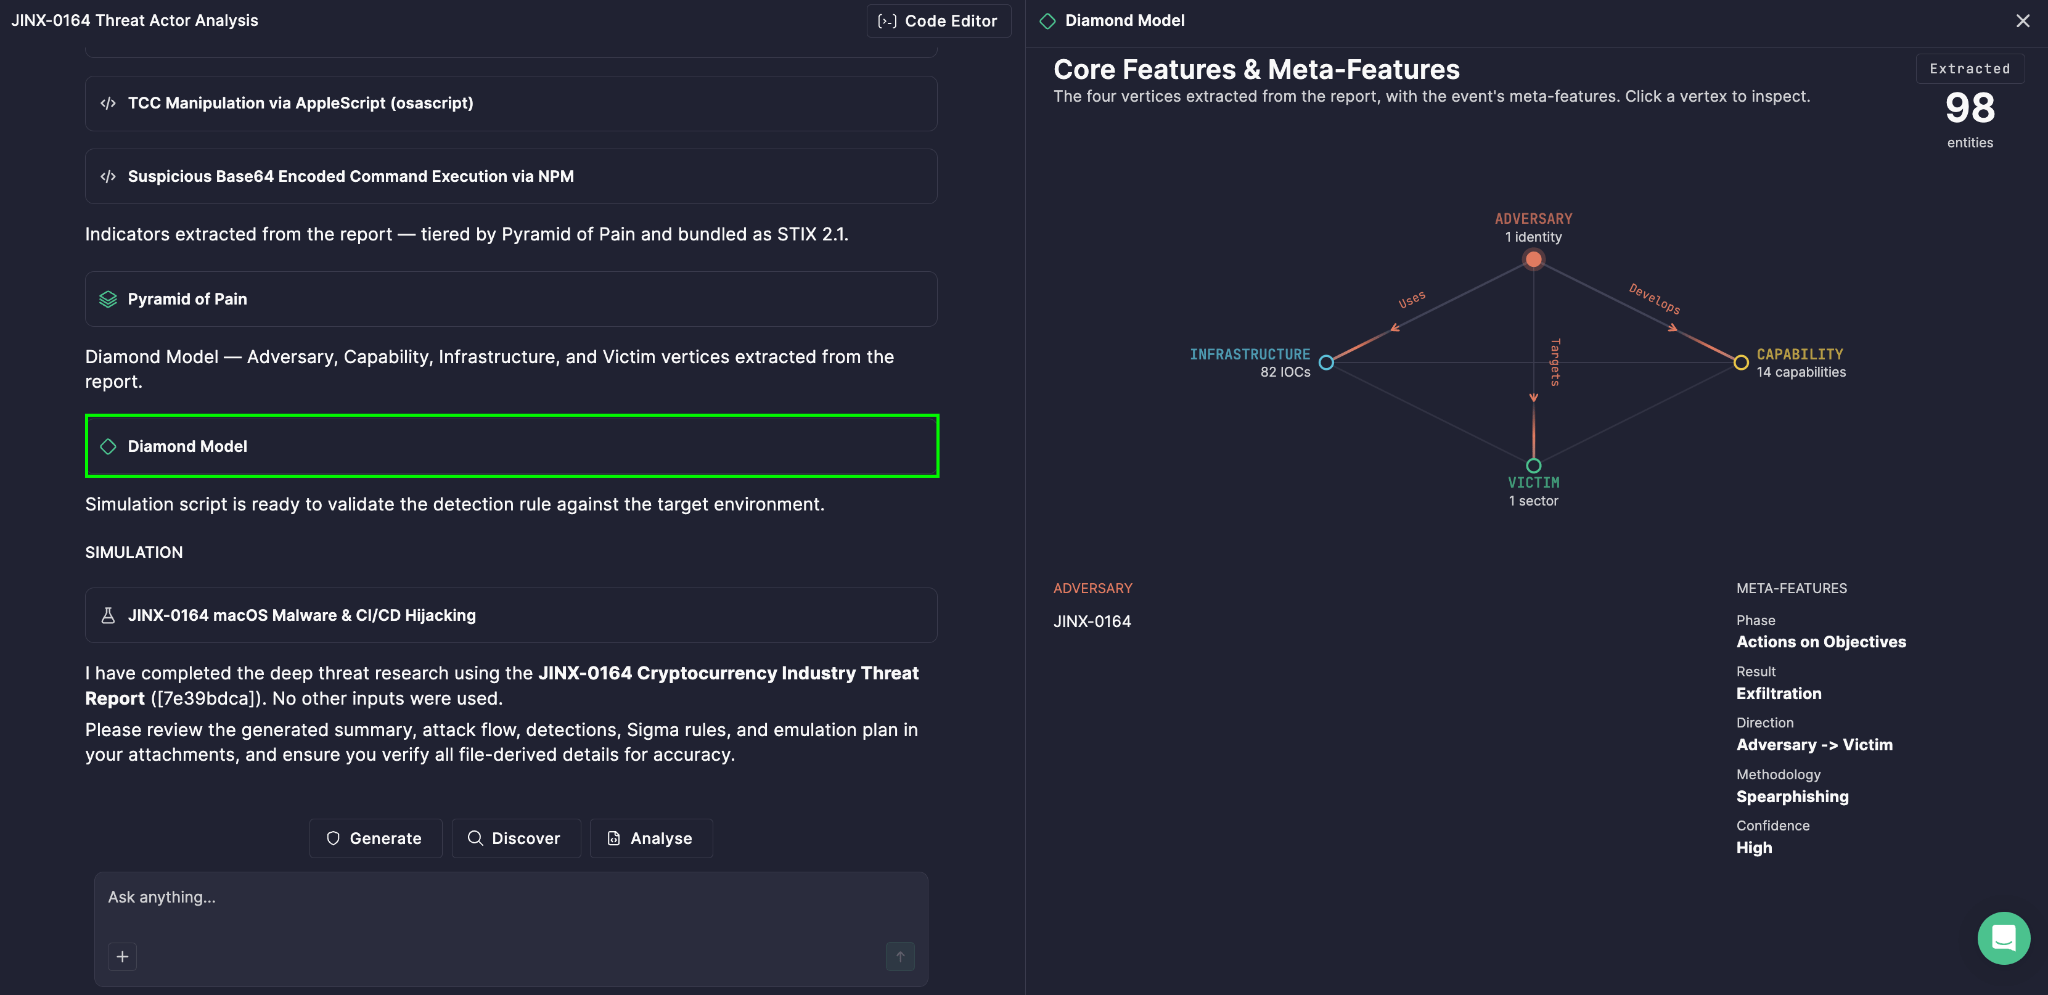
- Diamond Model – connects the four pillars of any intrusion — Adversary, Capability, Victim, and Infrastructure — and shows how they link together
Getting Started
Getting from a raw report to full threat intelligence takes just a few steps:
- Open Prime Architect and select the Agentic Threat Research mode.
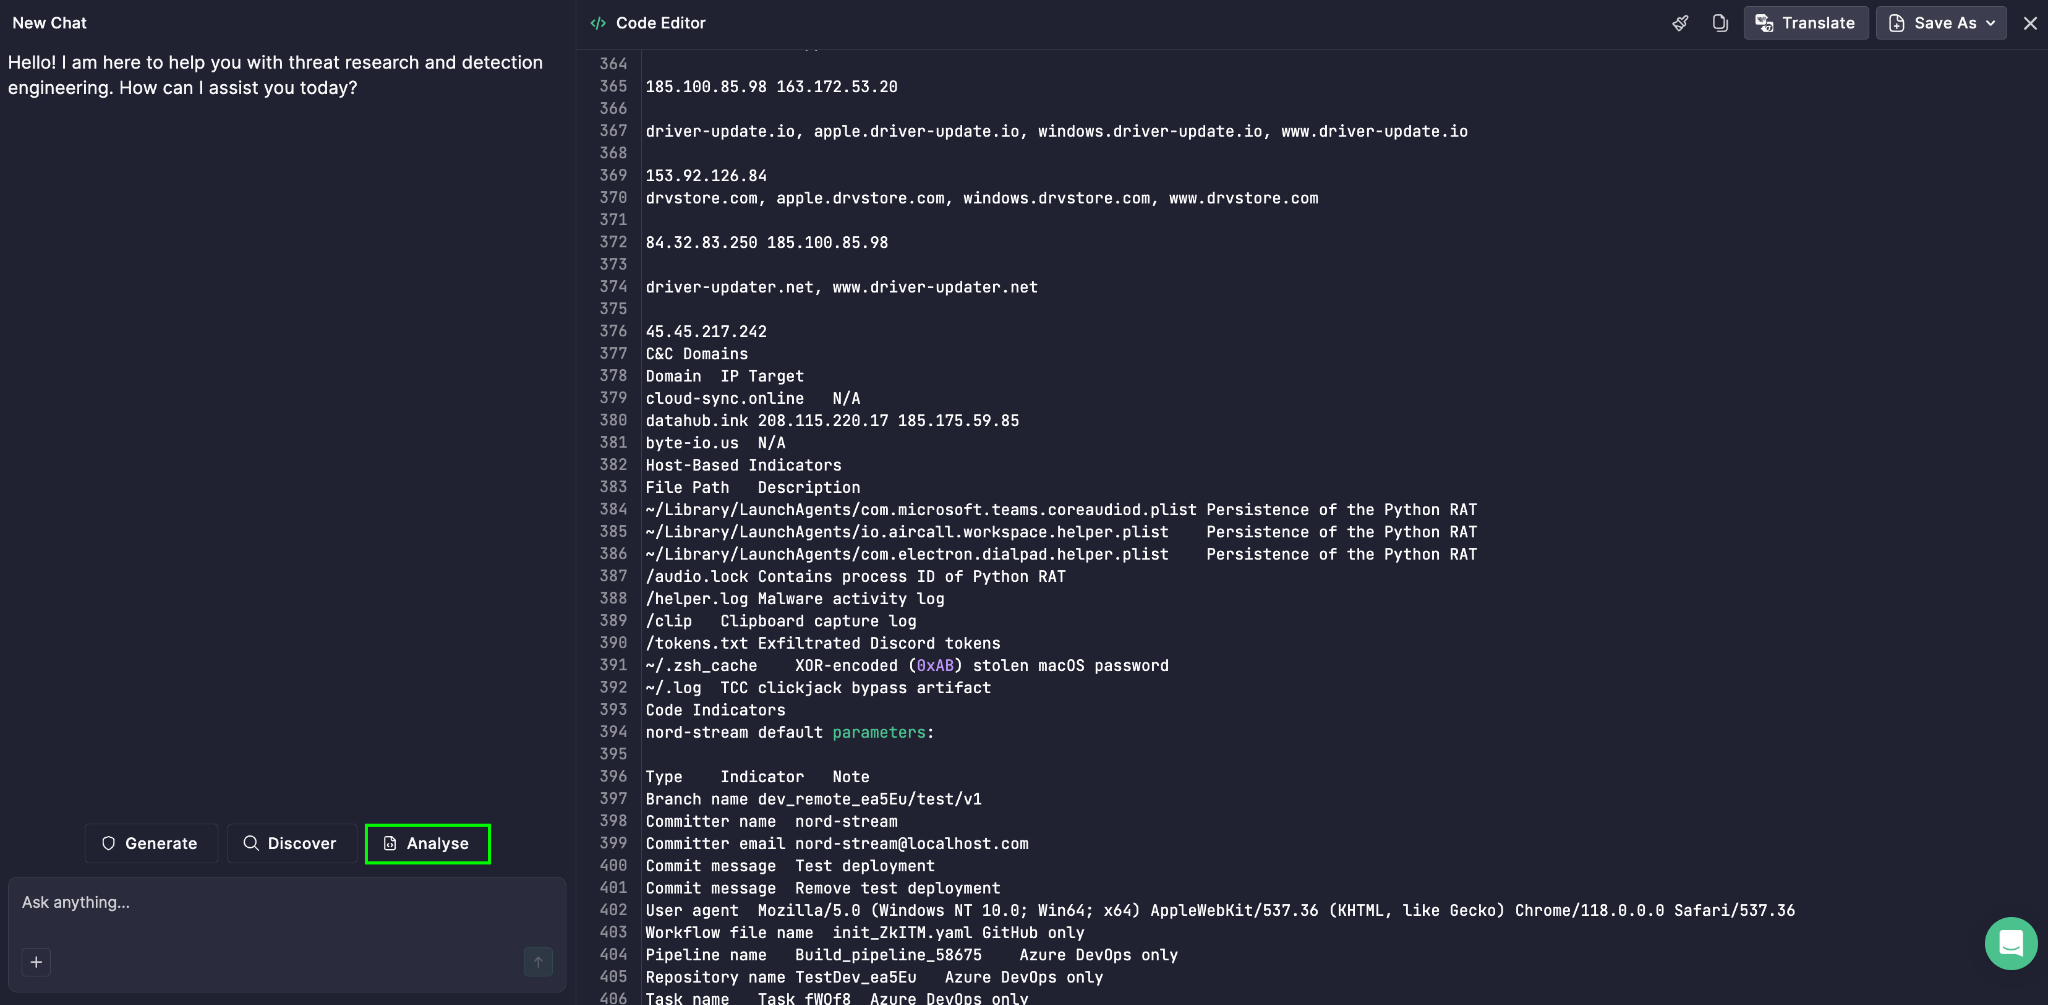
- Click Code Editor in the upper-right corner and paste in the text of your threat report.
- Select Analyze.
Key Takeaways
- SOCPrime explains how AI-powered deep threat research converts raw threat reports into actionable defense for overwhelmed security teams.
- The platform reduces hours of manual reading, cross-referencing, and translation of advisories into SOC actions.
- SOCs should adopt AI-assisted research tools to close the gap between threat intelligence publication and actionable defense.