A new extortion cocktail: office printers, small ransoms, and BitLocker
July 21, 2026 · Kaspersky (Securelist) · Severity: HIGH
The article details two incidents in Colombia and Mexico where attackers used corporate printers to notify victims of BitLocker encryption and demand ransom. The attackers exploited misconfigurations to deploy BitLocker and used printers to deliver ransom notes. This highlights a new extortion trend combining small ransoms with printer exploitation.
Recently, our teams in Latin America investigated a series of incidents involving misconfiguration, the deployment of BitLocker, and the exploitation of corporate printers. Attackers used the devices to notify organizations that their infrastructure had been compromised and they had to pay a ransom to recover their data.
This article analyzes two incidents that occurred in June in Colombia and in May in Mexico. We highlight the similarities in the attackers’ communications and outline emerging trends in ransom amounts.
Initial sign of an attack
In both cases, the affected users initially noticed a padlock icon next to their drives in Windows Explorer. This indicated that the drive was encrypted with BitLocker, blocking access to its contents.
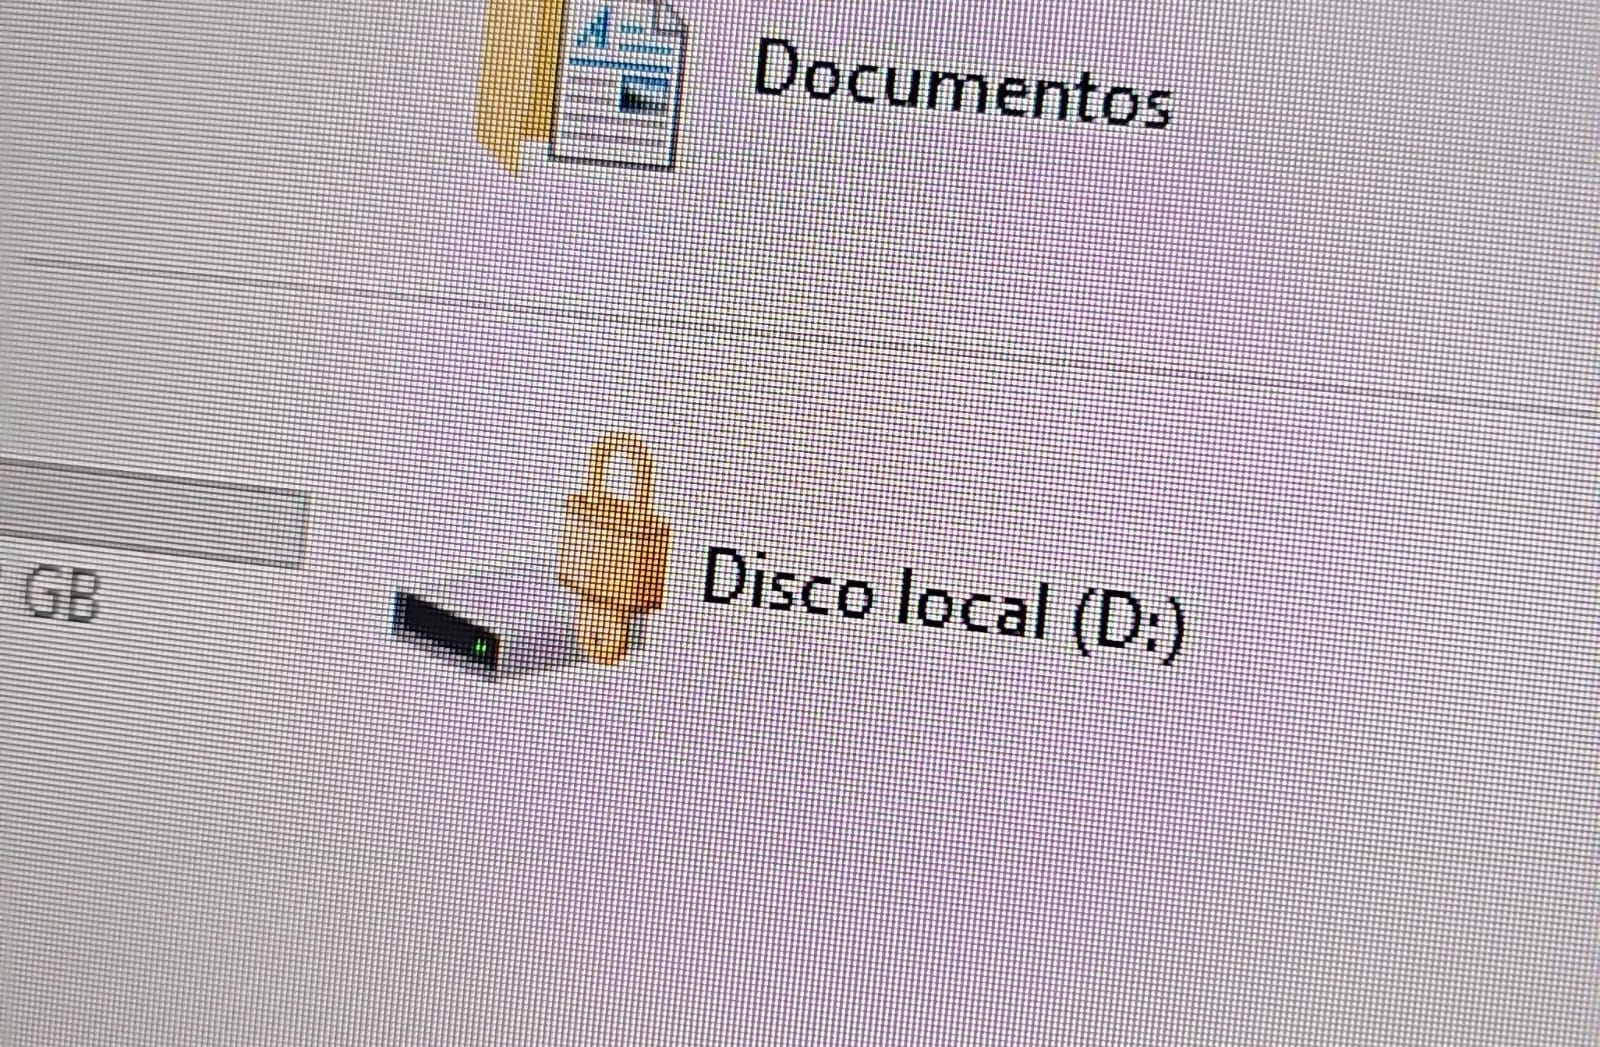
Drive icon indicating that the drive is locked
A recovery key was required to unlock the drive.
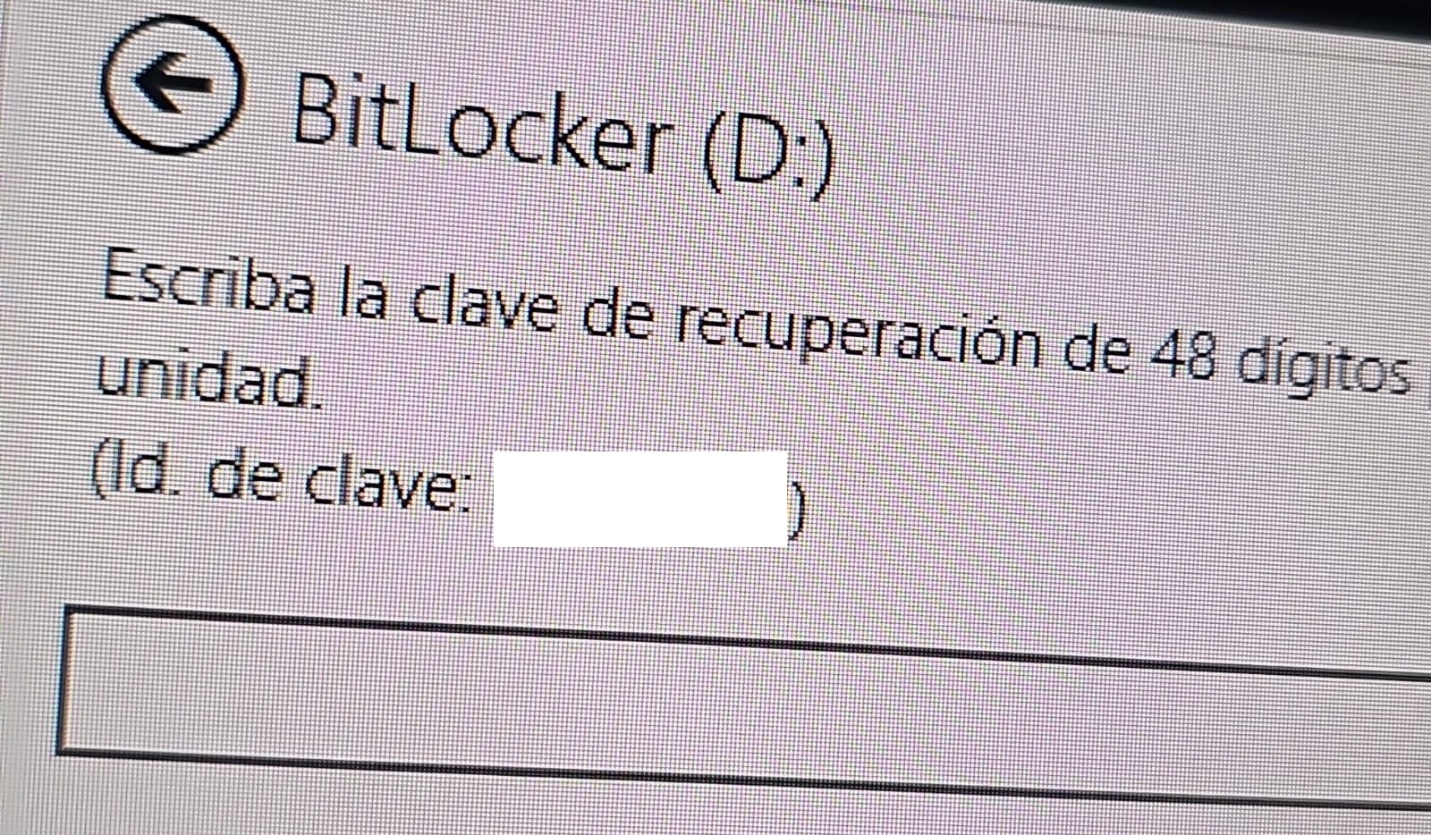
Attempt to access the disk’s contents and the prompt for the BitLocker recovery key
This is not the first time we have seen such threats; a few years ago, our team discovered a threat known as ShrinkLocker, which utilized BitLocker to achieve its goals.
First case: abusing RDP to encrypt data
One of the incidents occurred in Colombia in June. The attackers exploited an internet-exposed RDP service on a machine connected to an 8 TB storage device containing mission-critical data. After taking control of the system and manipulating user credentials, the attackers enabled BitLocker exclusively on the drive that primarily stored financial data. Once the encryption was complete, they locked the drive and used the company’s printers to produce ransom notes.

Ransomware note
Unfortunately, it was not possible to obtain evidence in the case due to the company’s rush to restore the encrypted disk. The communication with the attackers revealed a demand for just $3,000, and the company considered paying the ransom. After that, the system was restored before the forensic team could take any action, eliminating the evidence needed to assess the incident.

Attacker’s reply to the victim’s email sent to the address in the printed ransom note
This attack was made possible by an internet-facing remote desktop service (RDP) with additional open ports, which employees used to access corporate information. By exploiting this network exposure and misconfiguration, attackers breac
Key Takeaways
- Attackers exploit misconfigured corporate printers to deploy BitLocker encryption on victims' drives.
- Victims see a padlock icon on their drives, indicating encryption and blocked access to data.
- Ransom notes are printed via office printers, combining small ransoms with printer exploitation.